
ConnectWise Cloud Backup review: Supply-chain attack compromises Microsoft 365 tenants
In short
A compromised credential in ConnectWise Cloud Backup allowed unauthorized Microsoft Graph access across customer tenants in mid-October 2026.
ConnectWise Cloud Backup suffered a supply-chain compromise in October 2026 when attackers obtained a vendor-held credential tied to its Microsoft 365 app. The incident granted app-only access to Microsoft Graph in consenting tenants, exposing potential read and write capabilities to email, files, Teams data, and directory information without requiring user credentials or MFA bypasses.
ConnectWise Microsoft 365 breach timeline and scope
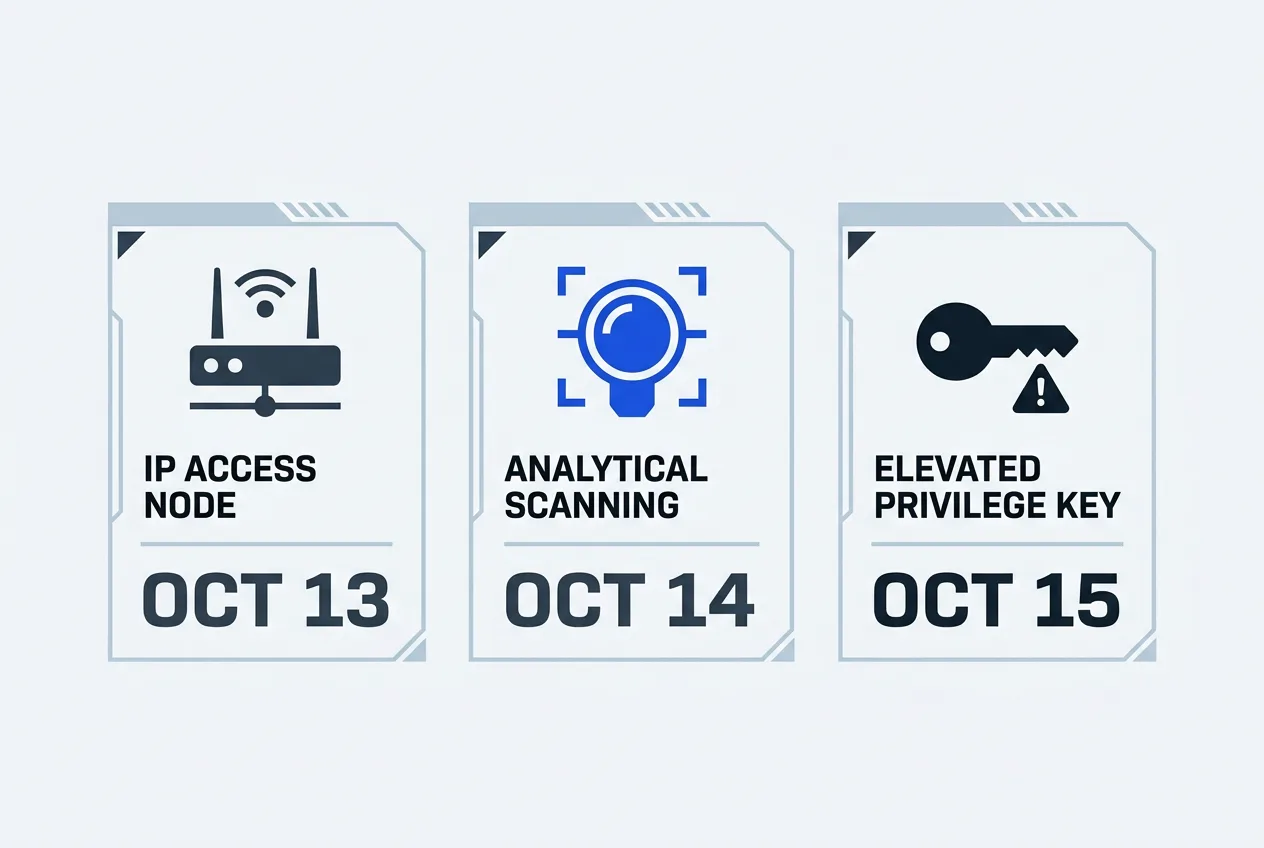
Activity began on October 13 with scripted sign-in attempts from IP 144.172.64.128. ConnectWise detected the issue on October 14. On October 15, service principals linked to the app self-assigned directory roles in affected tenants, including Exchange Admin and, in one case, Global Admin with added secrets set to expire in 2028. The main wave of unauthorized sign-ins occurred between 06:13 and 08:47 UTC, spaced roughly one to six minutes apart across tenants sorted by GUID.
Huntress confirmed unauthorized sign-ins in 162 to 173 tenants. Over 1,000 Entra tenants recorded sign-in activity from the primary attacker IP, with more than 300 successes. All tenants that had granted consent to the app (App ID 506e08f9-6e9a-4da4-942b-a099a03644ae) faced potential exposure. The attackers operated from rented hosting at RouterHosting AS14956 and later used additional IPs including 144.172.64.99 and 144.172.64.60.
ConnectWise disabled seven app identities on October 17, revoked associated certificates and credentials, and suspended Cloud Backup along with SaaS Security and Cloud Management services. Microsoft Threat Intelligence classified the event as an active supply-chain attack abusing a trusted OAuth application. No evidence emerged that attackers accessed encrypted backup archives, though scheduled backups and restores remained unavailable.
ConnectWise supply chain risks and user actions
The multi-tenant design of ConnectWise Cloud Backup required broad permissions across Exchange, OneDrive, SharePoint, Teams, and directory services to support backup functions. Storing the client assertion or API secret in the vendor environment created a single point that enabled cross-tenant access once compromised. App-only authentication inherently bypasses per-user controls, amplifying the reach of any stolen credential.
Partners should audit Entra sign-in logs for the listed app ID and review service principal activity since October 13. Key checks include added directory roles, new client secrets, and any OAuth consents granted to the affected app identities. ConnectWise advised customers to monitor the seven disabled app IDs and follow its technical guidance for containment.
As of October 19, services remained suspended while ConnectWise continued remediation with third-party support. No restoration timeline had been announced. Existing archives stayed isolated, yet organizations relying on the platform for Microsoft 365 protection faced operational gaps until validation completed.
- Review Entra sign-in logs for App ID 506e08f9-6e9a-4da4-942b-a099a03644ae
- Check for newly created client secrets or role elevations since October 13
- Verify current OAuth consents for Cloud Backup and related apps
- Monitor additional IPs reported in public advisories
| Date (UTC) | Event | Impact |
|---|---|---|
| Oct 13-14 | Initial sign-in attempts from 144.172.64.128 | Password spraying observed |
| Oct 15 | Role self-assignment and main sign-in wave | 162-173 tenants confirmed compromised |
| Oct 17 | App identities disabled, services suspended | Backups and restores halted |
Frequently asked questions
What permissions did the compromised ConnectWise app hold?
The app held broad consented permissions for mail, attachments, OneDrive and SharePoint files, Teams chats, and directory data through Microsoft Graph.
How many tenants showed confirmed unauthorized access?
Huntress reported between 162 and 173 tenants with confirmed unauthorized sign-ins from the affected app.
Did attackers access backup archives?
ConnectWise stated there was no observed unauthorized access to encrypted and isolated backup archives.
What should partners check in their Entra logs?
Partners should examine sign-ins for the specific App ID, added service principal roles, and any new client secrets created after October 13.
TrustScope
Comments 3