
ConnectWise Security Review: China-Linked AI Attack Hits MSP Cloud Backup Customers
In short
ConnectWise disclosed unauthorized access to Cloud Backup app identities in mid-October 2026. The incident involved China-linked actors using an AI framework against Microsoft 365 tenants managed by MSPs.
ConnectWise Security Review reveals that attackers gained access to application credentials for the Cloud Backup service in October 2026, allowing unauthorized sign-ins to customer Microsoft 365 environments. The company identified the activity between October 14 and 17, disabled affected app identities, and suspended the service on October 17. Phased restoration began on October 21 with security checks at each stage.
Existing backup archives stayed encrypted and isolated, with no evidence of compromise. ConnectWise serves managed service providers that rely on the tool to protect Microsoft 365 and Google Workspace data for business clients. The breach leveraged pre-granted app permissions rather than individual user accounts.
Incident Timeline and Containment Actions
ConnectWise detected suspicious activity on October 14 and 15. Confirmation of unauthorized access to seven app identities occurred between October 14 and 17. The company disclosed the issue on October 16 and suspended Cloud Backup along with two other services as a precaution on October 17. Twice-daily updates followed, and restoration started on October 21 with service-specific instructions released progressively.
Partners received guidance to keep connections disabled until cleared. ConnectWise stated that no other products showed signs of compromise. Microsoft 365 tenants without active backup subscriptions were still targeted in some cases. The rapid timeline left limited room for defenders to intervene before sign-in attempts occurred.
Customers should review Microsoft 365 sign-in logs, audit logs, app registrations, and permission assignments using the technical guide provided by ConnectWise. Additional checks for planted credentials or persistence mechanisms remain necessary even after service restoration.
Attack Method, Attribution, and Impact Scale
Microsoft attributed the operation to Storm-0940, a China state-aligned group active since 2021. The actors used the open-source ARTEX framework, which incorporates AI models to automate reconnaissance, password spraying, and OAuth app abuse at speeds reaching 2,900 attempts per minute. This approach reduced the time available for detection and response.
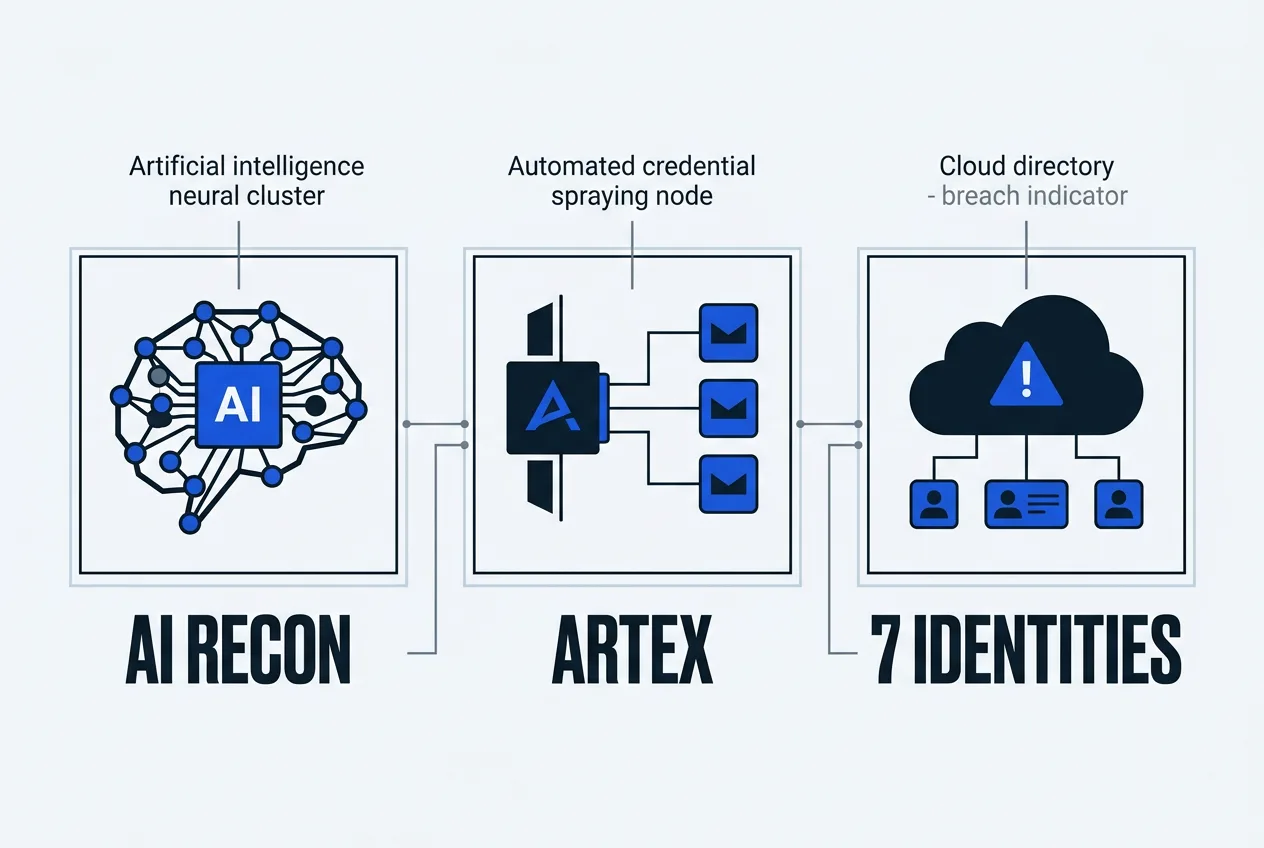
Attempts reached more than 2,250 Microsoft 365 tenants, with Huntress reporting activity against roughly 1,000 tenants and hundreds of successful authentications in its data. Follow-on actions included directory reconnaissance, credential modifications, and privilege changes in affected environments. Targets covered aerospace, defense, energy, finance, government, manufacturing, and technology sectors worldwide.
Successful authentication does not confirm data exfiltration. ConnectWise noted that evidence appears consistent with China state-aligned responsibility. The Chinese Embassy rejected the attribution. The incident underscores supply-chain risks for MSP platforms that hold broad tenant access through app permissions.
- Review all app registrations and revoke unused credentials immediately.
- Monitor Microsoft 365 audit logs for unusual Graph API or directory activity.
- Confirm that backup connections remain disabled until ConnectWise issues final clearance.
- Document any permission changes and retain logs for at least 90 days.
Practical Steps for MSPs and Tenant Owners
MSPs must independently validate tenant security before re-enabling any ConnectWise Cloud Backup connections. The company continues to issue updates on restoration progress. Broader industry attention now focuses on AI-accelerated attacks and the security posture of tools that receive delegated tenant permissions.
Organizations should maintain separate monitoring for OAuth app activity and consider limiting app permissions to the minimum required scope. Regular audits of third-party integrations reduce exposure in future incidents. ConnectWise has not reported compromise of backup archives themselves, but customer-side verification remains essential.
| Aspect | Details |
|---|---|
| Service affected | ConnectWise Cloud Backup (formerly SkyKick) |
| Access method | Compromised app credentials and OAuth permissions |
| Peak attempt rate | Up to 2,900 sign-ins per minute |
| Tenants targeted | Over 2,250 |
| Restoration start | October 21, 2026 |
Frequently asked questions
Is ConnectWise safe to use after the October 2026 incident?
ConnectWise disabled affected app identities and began phased restoration with security validation. MSPs must still review their own Microsoft 365 logs and permissions before re-enabling connections, as individual tenant checks remain necessary.
What data could have been exposed in the ConnectWise Cloud Backup breach?
Attackers obtained access to app identities that permitted sign-ins to Microsoft 365 tenants. This could include mailboxes, OneDrive files, SharePoint sites, Teams data, and directory information, though successful authentication does not confirm exfiltration.
How did the attackers use AI in the ConnectWise attack?
The group employed the ARTEX framework, which integrates AI models to automate reconnaissance and password spraying at high speed. Microsoft linked this method to Storm-0940 and noted similar prior use against South Korean financial systems.
What should MSPs check in their Microsoft 365 tenants now?
Review sign-in logs, audit logs, app registrations, and assigned permissions. Look for unexpected credential changes or privilege escalations. Retain logs for ongoing monitoring after any restoration.
TrustScope
Comments 1