
Genesys review: Internal CRM and LMS access incident of October 2026
In short
Genesys detected unauthorized access to internal CRM and learning systems on October 16, 2026. Core customer platforms remained unaffected.
Genesys reported unauthorized third-party access to certain internal business systems on October 16, 2026. The incident was limited to the company's customer relationship management platform and learning management system. No evidence emerged of continued access after containment.
Genesys Cloud, Genesys Engage, and Genesys Engage Cloud platforms showed no signs of compromise. Customer and partner environments hosted on those platforms stayed secure, including call recordings and analytics data.
What Happened in the Genesys Breach
The company confirmed that intruders accessed names, business email addresses, telephone numbers, job titles, company details, and other customer interaction records. These records belonged to existing and prospective customers stored in the internal systems. Genesys launched an investigation immediately upon detection and issued an official update on October 19, 2026.
An emerging group listed Genesys on a leak site around the same period and claimed additional data types such as contracts and password hashes. Genesys has not verified those broader claims, which exceed the confirmed scope of the internal CRM and LMS access.
Official statements emphasize that the incident involved only internal business systems. The company advised customers to monitor for suspicious communications and reiterated that it never requests passwords through unsolicited channels.
Is Genesys Safe for Enterprise Use
Core contact center platforms used by thousands of enterprises, including banks and telecom operators, remained isolated from the incident. Genesys stated there was no unauthorized access to customer data processed on the production environments. As of October 22, 2026, the investigation continues to determine the full scope of the internal breach.
Customers can distinguish between the affected internal tools and the unaffected cloud services by reviewing Genesys documentation on system architecture. No specific regulatory filings or individual customer notifications appear in public sources at this stage.
Businesses evaluating Genesys should track updates from the official blog for any new findings on data handling practices. The separation between internal administrative systems and customer-facing platforms provides a clear boundary for risk assessment.
Genesys CRM Security Review: Affected vs Unaffected Systems
Understanding the boundaries of the incident helps organizations decide on continued use. The following table summarizes confirmed details.
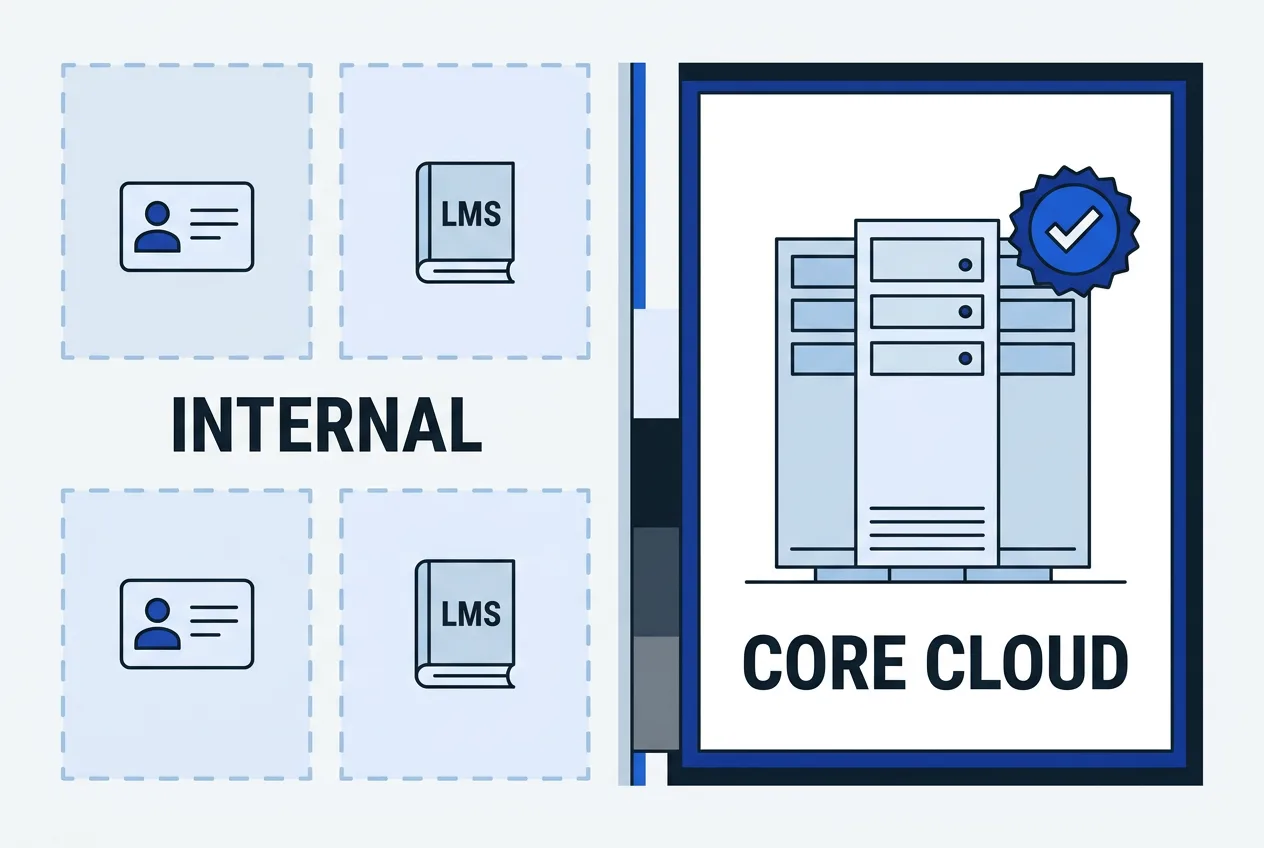
| Category | Affected | Unaffected |
|---|---|---|
| Internal CRM | Yes - names, emails, phone numbers, job titles | N/A |
| Learning Management System | Yes - training and interaction records | N/A |
| Genesys Cloud platform | No | Customer environments and analytics |
| Genesys Engage Cloud | No | Call recordings and partner data |
Enterprises should verify their specific deployment configurations directly with Genesys support. Regular reviews of access logs and multi-factor authentication settings remain standard practice for any CRM deployment. The October 2026 event highlights the importance of segmenting internal administrative tools from production customer systems.
Frequently asked questions
What data was accessed in the Genesys incident?
Genesys confirmed access to names, business email addresses, telephone numbers, job titles, and company account details stored in internal CRM and LMS systems. No customer production data from the cloud platforms was involved.
Were Genesys Cloud platforms compromised?
No. Genesys stated that Genesys Cloud, Genesys Engage, and Genesys Engage Cloud remained unaffected. Customer environments and call recordings stayed secure.
Has Genesys notified affected customers?
Public sources as of October 22, 2026, do not detail individual customer notifications or regulatory filings. The company issued a general security update advising vigilance for phishing attempts.
What should users do after the Genesys incident?
Monitor communications for suspicious activity and follow standard security practices. Organizations should contact Genesys support for deployment-specific guidance.
TrustScope
Comments 5