
GMO Onamae review: Security after October 2026 breach and bounty program
In short
GMO Onamae Desktop Cloud faced unauthorized access in October 2026 that exposed trading credentials for up to 26,739 servers. The company suspended services, offered compensation, and launched a $1 million bounty program.
GMO Onamae review focuses on the security failure in its Desktop Cloud service used widely for FX trading. Unauthorized access began around October 19, 2026, after a customer inquiry triggered the investigation. Malicious programs were confirmed on customer environments by October 20, leading to full service suspension on October 21.
GMO Onamae breach details and confirmed impacts
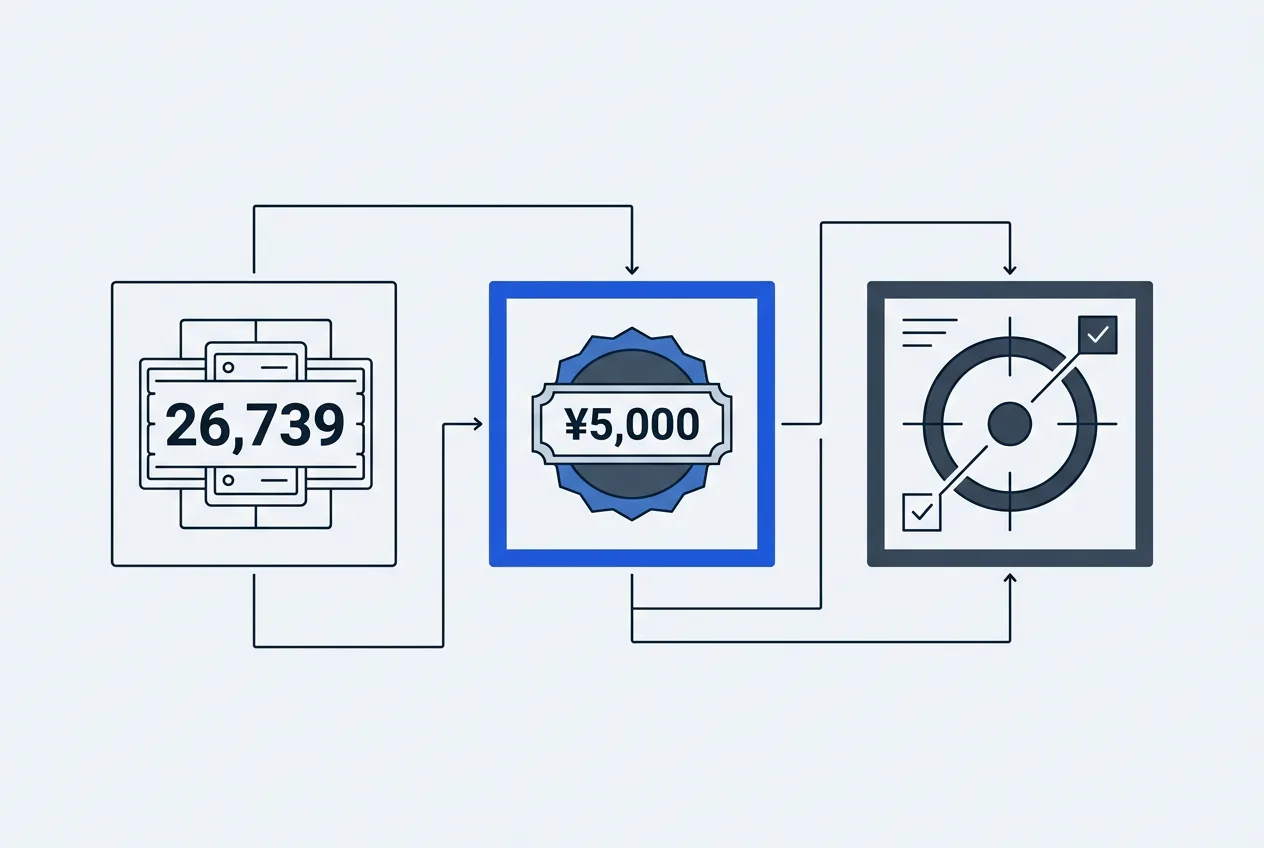
Attackers gained entry to the virtual Windows desktop service and installed malware that allowed viewing of stored trading account credentials. Up to 26,739 servers were potentially affected, though not all were confirmed compromised. The service supported automated trading tools such as MT4 and MT5 for customers of more than 70 securities and FX firms in Japan and overseas.
No payment card or credit data was stored on the affected servers. Confirmed damage included unauthorized trades reported by customers of five FX firms: Goldenway Japan, Oanda Japan, AvaTrade Japan, Gaitame Finest, and Dukascopy Japan. These firms responded with account suspensions and other protective measures. GMO stated that ransomware was not activated.
Key timeline points include the ransom demand of approximately 8 billion yen received on October 21 and the publication of claimed customer data on October 27. The leak site domain was taken down early on October 28. GMO shares dropped sharply in late October before partial recovery after the site takedown.
Compensation, service changes, and bounty program
GMO issued repeated apologies and adopted a no-ransom policy. All current customers received a flat goodwill payment of 5,000 yen. Verified trading losses and fees from unauthorized activity linked to the incident are eligible for full reimbursement. Additional payments ranging from 10,000 to 25,000 yen per information category, capped at 3 million yen per customer, apply to those whose data appeared in published leaks.
Customers received six months of free access to an alternative secure cloud desktop service for migration. GMO advised running full antivirus scans, backing up data, and changing passwords from secure devices. Police consultation began on October 22, and joint investigations with partners including Trend Micro continue.
The parent company GMO Internet Group launched the GMO Cybercrime Bounty program on October 28 offering up to 1 million USD for verifiable information leading to arrests or incident clarification. The program accepts tips through a dedicated portal until an arrest occurs or until October 27, 2027, and excludes tips from perpetrators. Within the first six hours, 113 tips had already been submitted.
Practical steps for current and former users
Users should verify any trading account activity since mid-October and contact their FX broker directly about potential exposure. Running malware scans on all devices that accessed the service remains essential even if no malware has been found on analyzed customer machines so far.
Those whose data appeared in leaks should document the categories disclosed and submit claims for the special goodwill payments. Monitoring for new leak sites is ongoing because the original domain was removed. Service resumption on the original infrastructure is not planned; a new secure platform is under development.
| Date | Event |
|---|---|
| Oct 19 | Investigation opened after customer report |
| Oct 20 | Malware confirmed on servers |
| Oct 21 | Full service suspension; ransom demand received |
| Oct 27 | Claimed data published online |
| Oct 28 | Leak site taken down; bounty program started |
Frequently asked questions
What data was exposed in the GMO Onamae breach?
Trading account login credentials stored on customer server environments were viewed. No payment card or credit data was stored on the affected servers.
How much compensation is GMO offering affected customers?
All current customers receive 5,000 yen. Verified trading losses receive full reimbursement. Additional payments up to 3 million yen apply for data appearing in published leaks.
Is the GMO Cybercrime Bounty program still active?
The program launched on October 28, 2026, and remains open until an arrest or until October 27, 2027. It offers up to 1 million USD for qualifying information.
Will GMO Onamae Desktop Cloud resume on the original infrastructure?
The service will not resume on the original setup. GMO plans a new secure platform and is offering six months of an alternative cloud desktop service to migrating customers.
TrustScope
Comments 1