
GoDaddy Certificate Revocation Incident: What Affected Customers Need to Know
In short
Over 400,000 GoDaddy and Starfield SSL certificates were revoked after a documentation mismatch. Affected customers must install replacements to restore secure site access.
GoDaddy certificate revocation affected 403,643 TLS certificates issued under its own and Starfield Technologies roots. The certificates contained policy information that did not match the published Certificate Policy and Certification Practice Statement documents. No keys were compromised and no evidence of unauthorized access was found.
The incident began when a third party reported discrepancies on October 14, 2026. GoDaddy confirmed the mismatch, suspended new issuance where required, updated the documents, and started mass revocation. By October 21 all affected certificates had been revoked or had already expired.
Breakdown of Affected Certificates
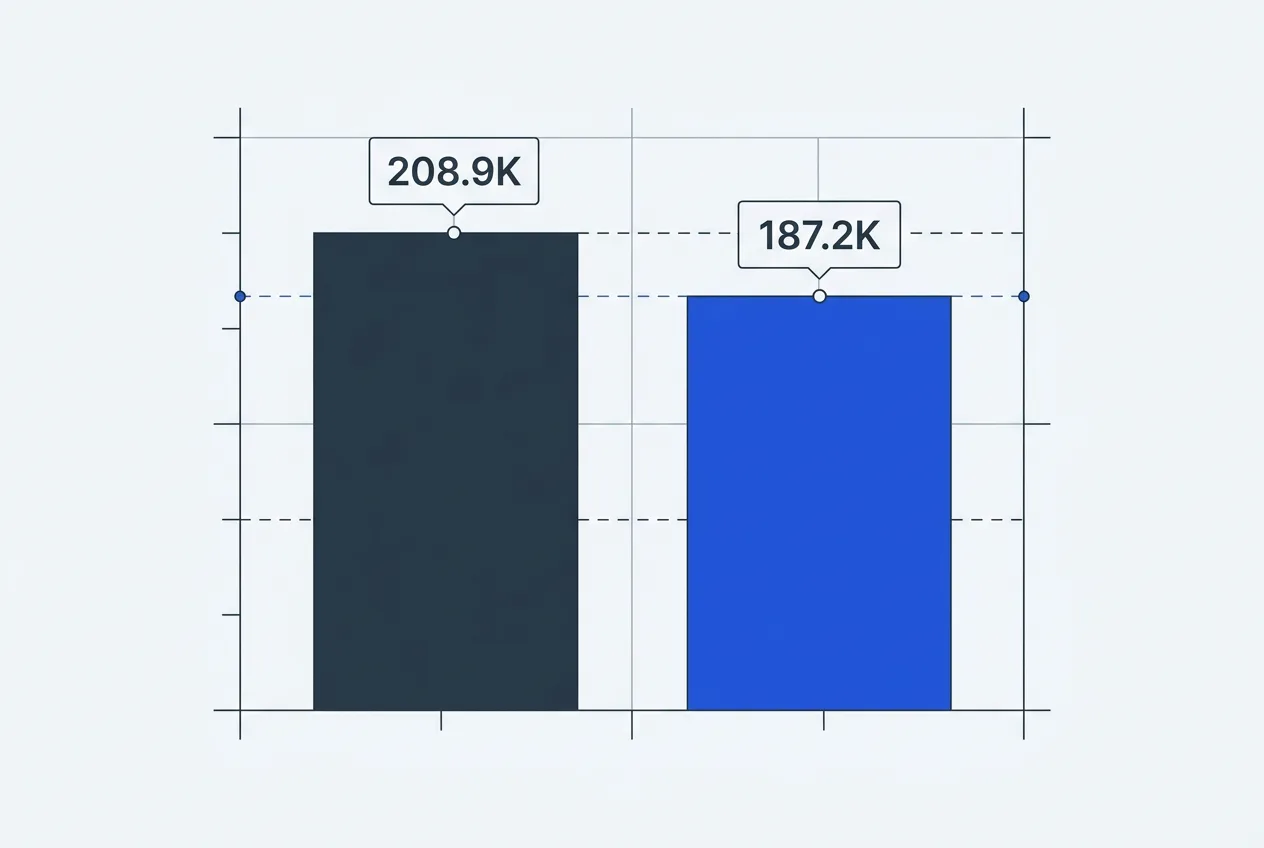
The revocation covered certificates across eight hierarchies. The largest groups were Starfield R1 DV certificates (208,900) and Starfield G2 DV certificates (187,200). Smaller numbers of organization-validated and extended-validation certificates were also included. Final counts showed 378,067 certificates revoked and 25,576 expired during the process.
| Hierarchy | Type | Approximate Count |
|---|---|---|
| Starfield R1 | DV | 208,900 |
| Starfield G2 | DV | 187,200 |
| Other hierarchies | OV/EV | 7,543 |
Revocation was required under CA/Browser Forum Baseline Requirements because the policy fields in the certificates did not align with the published CP/CPS. GoDaddy missed the five-day revocation deadline and completed the work on October 21, four days late. The reason code used was “superseded.”
Timeline and Browser Response
Initial outreach to affected customers started October 14. The required revocation deadline was October 18 at 23:45 UTC. Only about 170,600 certificates had been revoked by that point. Mozilla tracked the delayed revocations in public bug reports through October 22.
GoDaddy coordinated with high-volume customers in government, finance, and health sectors. Some Gibraltar government sites required immediate replacement. Affiliates such as Host Europe and DomainFactory also notified their customers. No issuance was halted on the G2 hierarchy after the initial suspension.
Actions for Site Owners
Customers should check certificate status through their GoDaddy account or the ssltools.godaddy.com/cert-check tool. Any certificate listed as revoked or superseded must be replaced immediately. Sites using the old certificates will display browser warnings until new ones are installed and propagated.
GoDaddy has stated it will publish a full incident report. In the meantime, status pages note ongoing SSL service degradation for some customers. Replacement certificates carry the same validity periods as the originals and can be downloaded from the same management interface.
Site owners should verify that their web server configuration references the new certificate files and that intermediate chains are updated. Testing with tools such as SSL Labs or openssl s_client confirms that the replacement has taken effect and that no policy mismatch warnings remain.
Frequently asked questions
Why were so many GoDaddy certificates revoked?
The certificates contained Certificate Policy fields that did not match GoDaddy’s published CP/CPS documents. Baseline Requirements mandate revocation when such mismatches occur.
Did the revocation indicate a security breach?
No. The issue was limited to documentation compliance. There was no evidence of key compromise or unauthorized issuance.
How long do customers have to replace certificates?
Revocations were completed on October 21, 2026. Sites using revoked certificates already show browser warnings, so immediate replacement is required.
Which certificate types were most affected?
Domain-validated certificates under Starfield R1 and Starfield G2 roots accounted for the large majority of the 403,643 total.
TrustScope
Comments 1