
Gyazo Security Review: 23.6 Million Records Exposed in September 2026 Breach
In short
Helpfeel reported a September 2026 breach that exposed 23.62 million Gyazo account records and limited image metadata after a server vulnerability was exploited.
Gyazo security review shows that Helpfeel Inc. disclosed unauthorized access to its image upload server on September 11, 2026. Attackers exploited a vulnerability in image and video conversion processing, extracted data from the database, and viewed 432 image files belonging to 133 users. The company blocked access and applied a patch within hours, then issued three public updates through October 21.
The incident affected approximately 23.62 million account records. Of these, 18.01 million belonged to anonymous accounts without email addresses. The remaining 5.62 million accounts included registered email addresses. No credit card numbers were stored or exposed.
Gyazo Security Review: Scope of Exposed Data
Account records contained varying combinations of name or nickname, email address, password hash, user and device identifiers, login session tokens, X integration tokens, Google SSO email where linked, profile details, language preference, registration and login timestamps, subscription plan, billing status, and usage statistics. Password hashes were not accompanied by any plaintext credentials.
Image metadata exposure reached roughly 490 million records for images uploaded on or before January 2019. Additional smaller sets covered 2.4 million records meeting specific filter criteria and 174 million records for images deleted on or before February 2023. Metadata fields included image IDs that could allow URL reconstruction, upload IP addresses, User-Agent strings, EXIF location data when present, OCR-extracted text, titles, source URLs, and hashed passphrases for private images. Forensic analysis found no evidence of mass image file exfiltration.
The following table summarizes the main data categories and their scale.
| Category | Approximate Volume | Key Fields |
|---|---|---|
| Account records | 23.62 million | Email, password hash, session IDs, SSO tokens |
| Image metadata (pre-2019) | 490 million | Image ID, upload IP, EXIF, OCR text |
| Deleted image metadata | 174 million | Image ID, hashed passphrase |
| Confirmed image files viewed | 432 files (133 users) | Full image content |
Helpfeel reported the incident to Japan’s Personal Information Protection Commission on September 15 and submitted follow-up notices on September 24. The company also notified roughly 30 overseas data protection authorities and consulted Kyoto Prefectural Police. As of October 20, no confirmed secondary harm or dark-web listings had been identified.
Gyazo Response Actions and Current Status
Service-wide security verification followed the initial patch. The platform was suspended on September 18 as a precaution and restored on September 27 with images initially restricted to owner-only viewing. Notifications began rolling out around September 20 to users with registered emails; in-app notices reached anonymous accounts. Users received advice to change Gyazo passwords and any reused elsewhere.
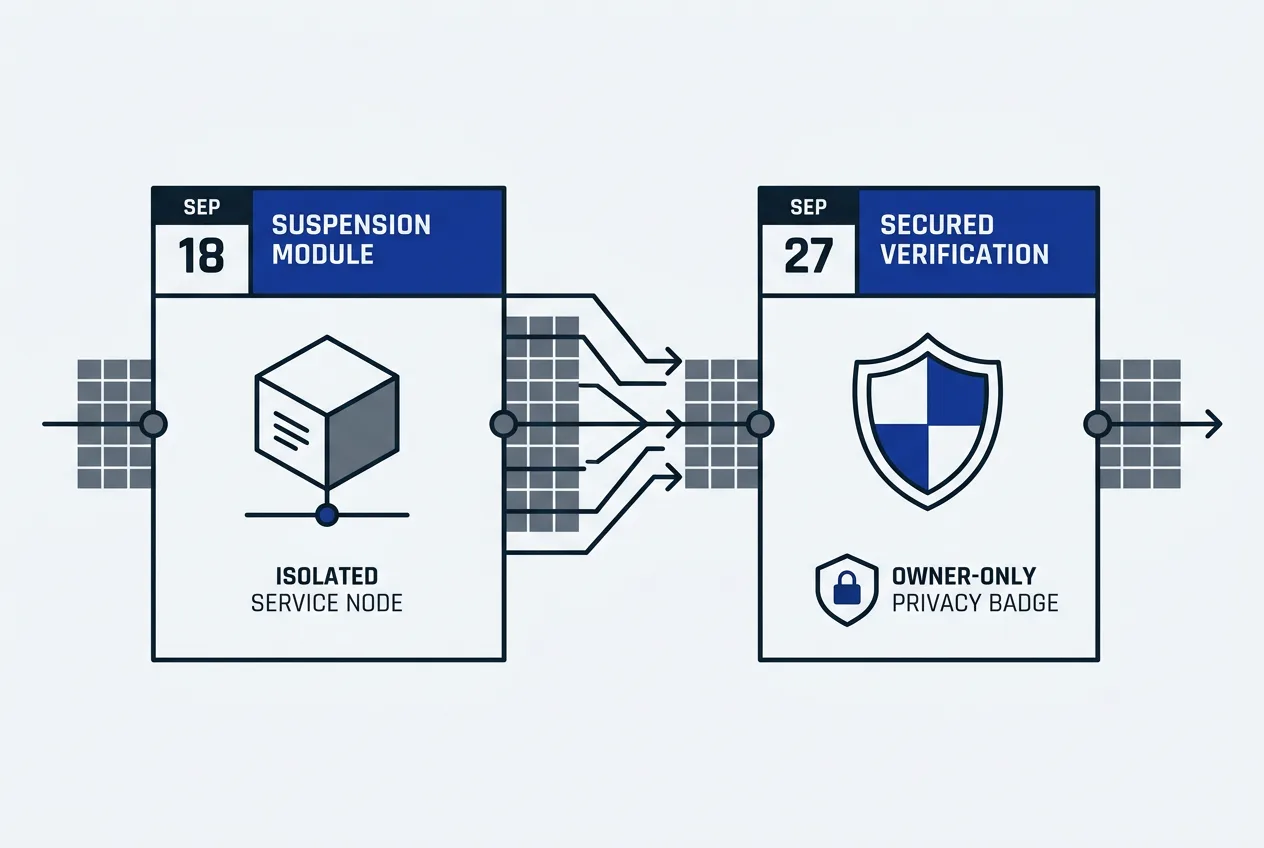
Further steps include continued monitoring for at least one year, implementation of stricter data retention policies, enhanced access controls, and staff training. The October 21 update stated that third-party forensic findings on the 133 affected users had been completed and positioned the report as final on investigation results, with updates promised only for new material facts.
Users checking Gyazo review sources should verify whether they received direct notification and confirm that any linked X or Google accounts have not shown unusual activity. Password changes and monitoring of associated email accounts remain the primary recommended steps.
Frequently asked questions
What exactly was exposed in the Gyazo breach?
Account records for 23.62 million users and metadata for hundreds of millions of images were accessed. Only 432 image files linked to 133 specific users were confirmed viewed by the attacker.
Did the breach include payment information?
No credit card numbers or payment card data were stored in the affected systems, according to Helpfeel’s October 21 report.
Has Gyazo fixed the vulnerability?
The exploited flaw in the image upload server was patched within hours on September 12. Additional security measures and monitoring remain in place.
Should users change their Gyazo password?
Helpfeel advised all users to update their Gyazo password and any reused passwords on other sites. Notifications continue on a rolling basis.
TrustScope
Comments
No comments yet. Be the first!