
Nikkei Security Review: Third Data Breach in a Month Exposing 1.8 Million Records
In short
Nikkei disclosed a cloud service breach on October 16, 2026, that exposed 1.83 million records. The incident follows two earlier compromises within roughly a month.
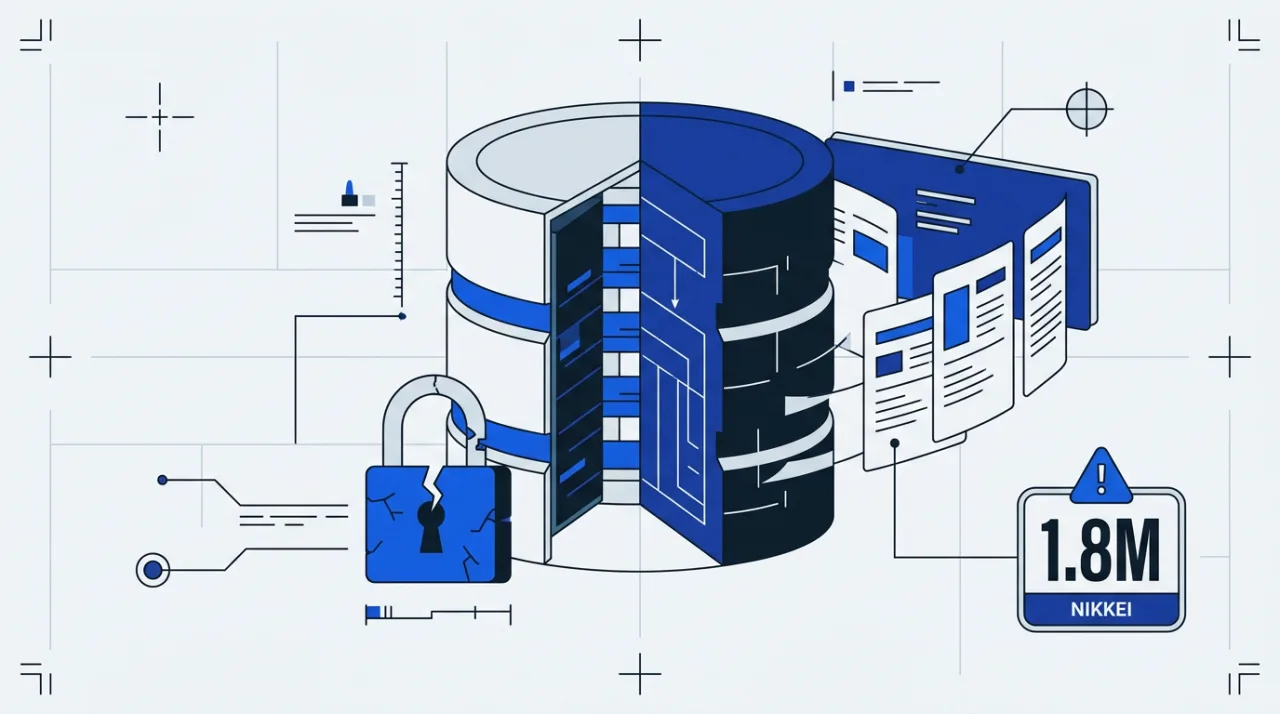
Nikkei Inc. disclosed on October 16, 2026, unauthorized access to a cloud service used for system development that exposed approximately 1.83 million personal information records. The company detected the intrusion on October 7 and disabled the stolen credentials immediately. No evidence of data misuse or tampering has appeared so far.
Nikkei Breach Details and Impact
The access occurred between the early hours and morning of October 7, 2026. Attackers used stolen credentials, though the method of theft remains unknown. Nikkei reported the incident to Japan’s Personal Information Protection Commission on October 11 and began notifying affected individuals.
Of the exposed records, roughly 1.68 million contained only non-identifying information. The remaining 150,000 included at least one identifier such as name, email address, postal address, phone number, or date of birth. About 120,000 of those records contained email addresses. No credit card data was involved.
Nikkei stated that affected people will receive direct notifications and that the company continues to review the full scope. As of the disclosure date, the organization found no signs of system outages, data tampering, or misuse of the leaked information.
- 1.68 million records: non-identifying data only
- 150,000 records: at least one personal identifier
- 120,000 records: included email addresses
- Zero credit card or payment details exposed
Pattern of Recent Incidents at Nikkei
The October 7 breach marks the third disclosed cybersecurity incident for Nikkei within roughly a month. In late July, a Google Workspace compromise affected about 1,646 people. A late-September Microsoft 365 account hijack allowed attackers to send approximately 9,000 phishing emails.
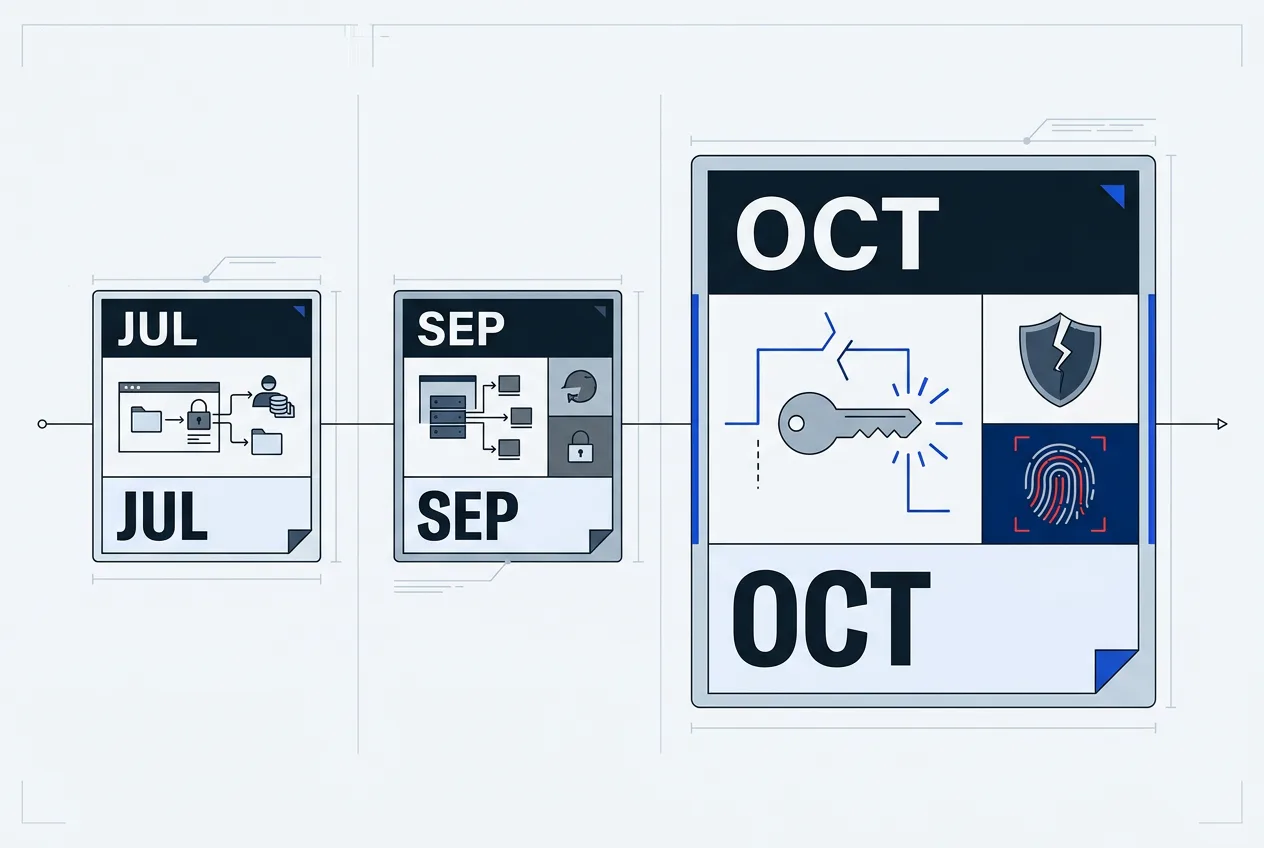
The company has apologized publicly and stated it will strengthen security measures. No service disruptions occurred during any of the three incidents. The recent wave of Japanese corporate breaches often involves credential compromise or cloud configuration issues, and Nikkei experienced a prior Slack-related breach in 2025.
| Incident Date | Platform Involved | Records or Impact | Key Details |
|---|---|---|---|
| Late July 2026 | Google Workspace | ~1,646 people | Unauthorized access |
| Late September 2026 | Microsoft 365 | ~9,000 phishing emails | Account hijack for spam |
| October 7, 2026 | Cloud development service | 1.83 million records | Stolen credentials |
Assessing Nikkei Data Protection Practices
Nikkei has committed to reviewing its security posture after each incident. The organization continues its investigation and plans additional protective steps. Users whose information was exposed should watch for unusual account activity and consider enabling multi-factor authentication where possible.
Broader reporting on Japanese corporate incidents in September and October 2026 shows repeated credential-based attacks and cloud misconfigurations. Individuals and businesses that interact with Nikkei services can reduce exposure by using unique passwords and monitoring official notifications from the company.
Organizations evaluating media and data-handling partners may review Nikkei’s public incident statements for transparency on response timelines and data categories affected. The absence of payment data in this latest breach limits certain financial risks for those whose records were exposed.
Frequently asked questions
What happened in the latest Nikkei breach?
Unauthorized access via stolen credentials on October 7, 2026, exposed 1.83 million records from a cloud service used for development. The company disabled the credentials and reported the incident to regulators.
How many records contained personal identifiers?
About 150,000 records included at least one identifier such as name, email, address, phone, or date of birth. Roughly 120,000 of those contained email addresses.
Has Nikkei faced other breaches recently?
Yes. Two earlier incidents occurred in late July and late September 2026, involving Google Workspace and Microsoft 365 accounts respectively.
What should affected individuals do?
Monitor accounts for unusual activity and follow any direct notifications from Nikkei. The company plans individual outreach to those whose data was exposed.
Does the breach include financial data?
No credit card or payment information was involved in the October 2026 incident.
TrustScope
Comments 5