
Quest Diagnostics breach
In short
Quest Diagnostics reported unauthorized access to its Quanum Lab Services Manager system on October 21, 2026. The incident involves certain patient records used by healthcare providers for lab orders and results.
Quest Diagnostics disclosed unauthorized access to its Quanum Lab Services Manager platform on October 22, 2026. The company learned of the incident the previous day and immediately paused access to the affected system while notifying law enforcement and engaging external cybersecurity experts.
The breach centers on the Quanum LSM tool, which some healthcare providers use to order tests and retrieve results. Core laboratory operations and direct connections to electronic medical records systems continued without interruption.
Scope and response to the Quest Diagnostics breach
Quest stated that an unauthorized party accessed certain patient records, which may contain protected health information. Investigators have not yet determined the exact number of records involved, whether data was copied, or the full list of data elements exposed. The company continues to examine logs and restore controlled access.
Official notices emphasize that the incident has not materially disrupted patient services. Quest has filed the required SEC disclosure and confirmed the event is unrelated to recent vulnerabilities in PHP software. Providers relying on the platform received direct communications about the temporary suspension.
Healthcare organizations should review their own access logs for the period before October 21 and confirm whether any Quanum LSM accounts showed unusual activity. Patients who received lab services through affected providers may receive notifications later if regulators require them.
Comparison with earlier Quest Diagnostics incidents
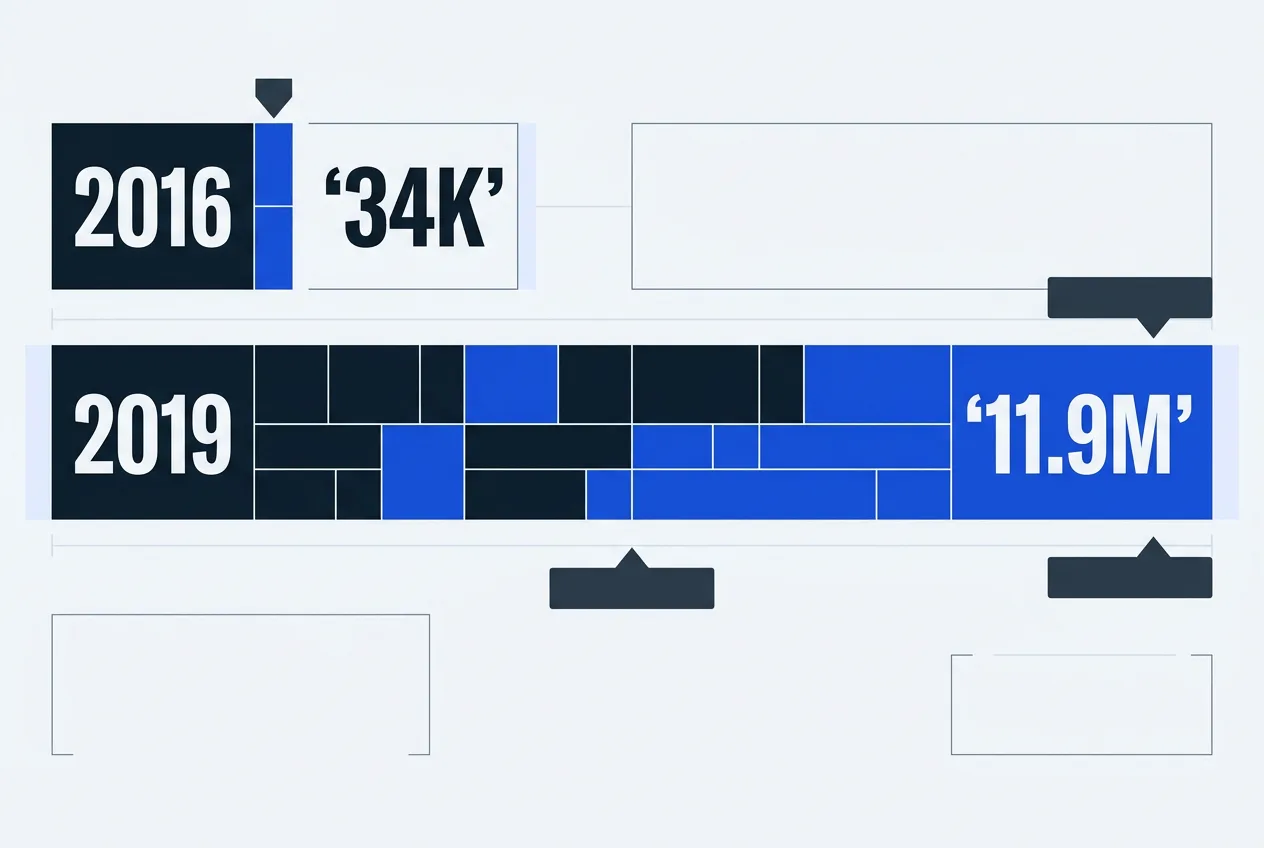
Quest has managed previous security events. The 2016 breach exposed lab results and contact details for roughly 34,000 individuals. A 2019 vendor incident affected approximately 11.9 million patients when a third-party system was compromised.
| Year | Incident type | Records affected | Key impact |
|---|---|---|---|
| 2016 | Direct system breach | ~34,000 | Lab results and contact data exposed |
| 2019 | Vendor-related exposure | ~11.9 million | Patient information accessed via third party |
| 2026 | Quanum LSM access | Under investigation | Patient records in lab ordering platform |
These events illustrate the recurring challenge of protecting laboratory data systems that connect multiple healthcare entities. Current monitoring focuses on whether the latest incident involves data exfiltration, a factor absent from the initial public statements.
Practical steps for providers and patients
Healthcare practices using Quanum LSM should maintain alternative ordering channels until Quest confirms full restoration. They can also request written updates on the investigation timeline and any regulatory filings that follow.
Patients concerned about their records should contact the ordering physician or Quest directly for information on potential notifications. Monitoring credit reports and explanation-of-benefits statements remains advisable even without confirmed numbers of affected individuals.
The ongoing investigation will determine whether additional disclosures or corrective measures are required under HIPAA and state breach notification laws.
Frequently asked questions
What systems were affected in the Quest Diagnostics breach?
The breach involved the Quanum Lab Services Manager platform used by some providers to order tests and view results. Direct laboratory information systems and electronic medical record connections were not impacted.
How many patient records were exposed?
Quest has not released confirmed numbers. Investigators continue to determine the exact scope of accessed records and whether any data left the system.
Is Quest Diagnostics still operating normally?
Core lab testing and most interfaces continue without material disruption. Access to the Quanum LSM tool was paused while the company investigates and restores controlled use.
What should providers do after the Quest Diagnostics breach?
Review access logs for unusual activity, maintain backup ordering methods, and request written status updates from Quest on investigation progress and any required notifications.
TrustScope
Comments 3