
So-net Security Review After October 2026 ISP Customer Database Breach
In short
The October 2026 So-net breach exposed membership details for over 2.5 million records. Official statements confirm limited data types and rapid containment measures.
So-net experienced unauthorized access to its member database on October 19, 2026. The incident affected 2,585,481 records across So-net and plala services, with confirmation and server isolation completed within days.
So-net Data Breach Scope and Exposed Information
The breach targeted membership records held by Sony Network Communications. Current and former subscribers who canceled after March 2026 had their information stored for billing and support purposes, which contributed to the total count. No login passwords for active member accounts or credit-card details appeared in the leaked set.
Exposed fields included names, phone numbers, email addresses, user IDs, dates of birth, gender, and internet connection IDs. Separately, four legacy email services yielded 54,401 email-and-password combinations. Those passwords received immediate forced resets on October 27. Sixteen bank-account records without PINs and seven password-reset notices also surfaced in the data.
Company statements list the cause as third-party unauthorized access under ongoing investigation. The Personal Information Protection Commission received formal notification. No secondary harm such as confirmed account takeovers had been reported by October 29.
- Names, phone numbers, and email addresses
- User IDs and internet connection IDs
- Dates of birth and gender
- Limited legacy email credentials
- Sixteen bank records without PINs
Company Response and Containment Actions
So-net isolated the affected server on the day of detection and blocked attacker traffic. Individual notifications went out to impacted users, including physical letters for the bank-record cases. A dedicated FAQ page and hotline opened immediately after disclosure on October 27.
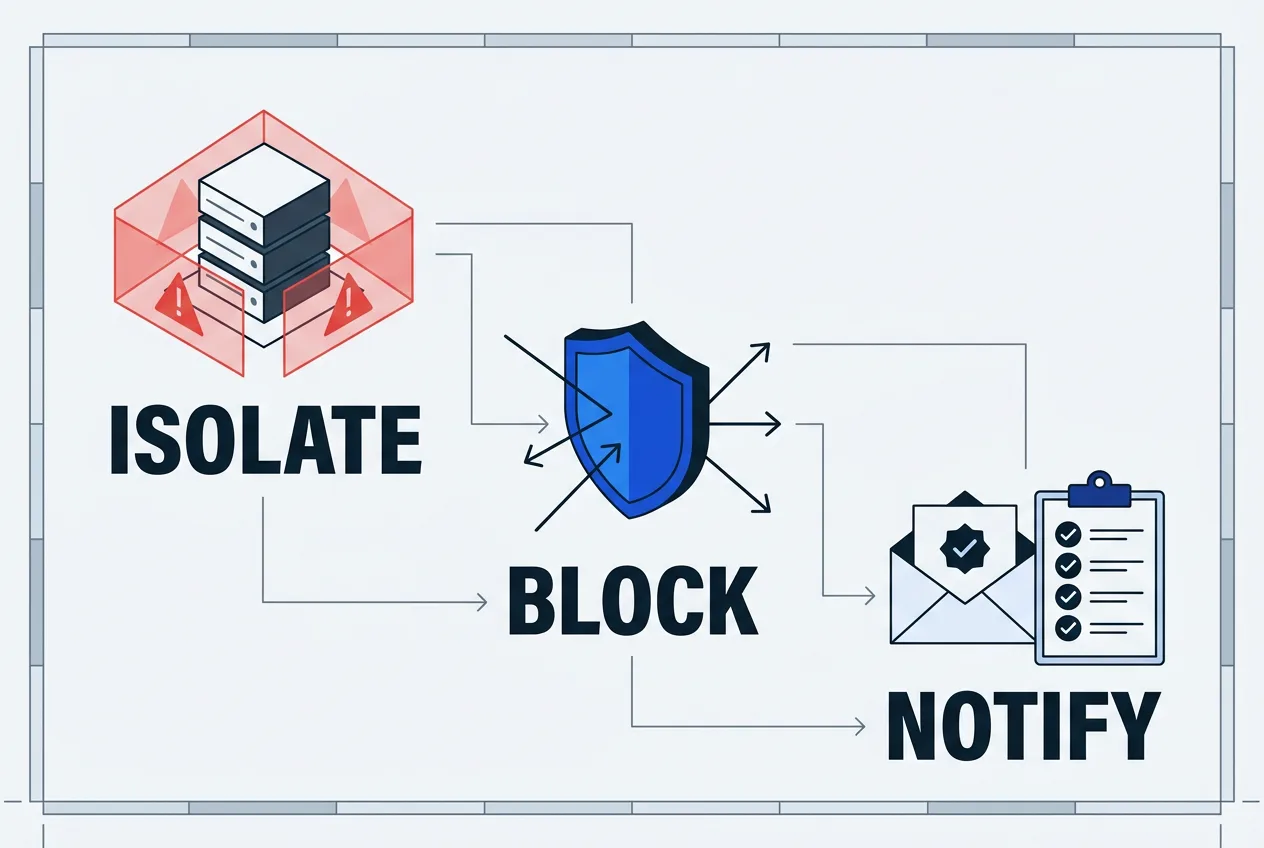
Users received instructions to ignore unsolicited contacts, avoid clicking links, and manually enter the official My Page URL when resetting passwords. NURO and other Sony Network services remained unaffected. The company stated it would review its security measures and information-management systems.
As of November 2, 2026, the internal and regulatory investigations continue. Further updates are expected through official news releases. No lawsuits or compensation programs have been announced.
Privacy Concerns and Practical User Steps
The incident highlights risks tied to retained former-customer data and legacy service credentials. Although core login passwords stayed protected, the volume of names, contact details, and birth dates creates potential for targeted phishing or social-engineering attempts.
So-net advises customers to monitor accounts closely and reset any affected legacy passwords through verified channels. The company warns of possible future impersonation calls or messages using the leaked information. Users outside Japan should verify whether their data was included by contacting the hotline or checking the published FAQ.
Ongoing transparency from the provider will determine long-term trust. Monitoring official channels remains the most direct way to stay informed about investigation outcomes and additional security updates.
Frequently asked questions
What data was taken in the So-net breach?
Membership records included names, phone numbers, email addresses, dates of birth, gender, and connection IDs. Legacy email passwords from four older services and sixteen bank records without PINs were also exposed. Active member login passwords and credit-card data remained protected.
How did So-net respond to the October 2026 incident?
The company isolated the server the same day, blocked attacker traffic, reset affected passwords, and notified users. It opened a hotline and FAQ page while reporting the event to Japan’s Personal Information Protection Commission.
Are So-net services still safe to use after the breach?
Core login systems and payment data stayed secure. The provider has implemented containment steps and advises standard precautions such as ignoring suspicious messages. Continued monitoring of official updates is recommended.
What should affected So-net users do now?
Users should reset legacy email passwords via the official site, watch accounts for unusual activity, and ignore unsolicited contacts. The hotline 0120-36-8887 and FAQ page provide further guidance.
TrustScope
Comments 1