
TrustBank review: 4.45 Million Donor Records Exposed in Furusato Choice Breach
In short
TrustBank reported unauthorized access to its Furusato Choice platform on October 17, 2026, resulting in the exposure of 4.45 million donor records including names, addresses, and hashed passwords.
Incident Details and Data Exposure
TrustBank Inc., the operator of Japan's Furusato Choice platform, confirmed on October 20, 2026, that unauthorized access occurred three days earlier. The breach affected 4,454,097 records of members and donors. Exposed information includes names, email addresses, physical addresses, telephone numbers, hashed passwords, and estimated donation tax-deduction amounts. No payment card or credit data was involved in the leak.
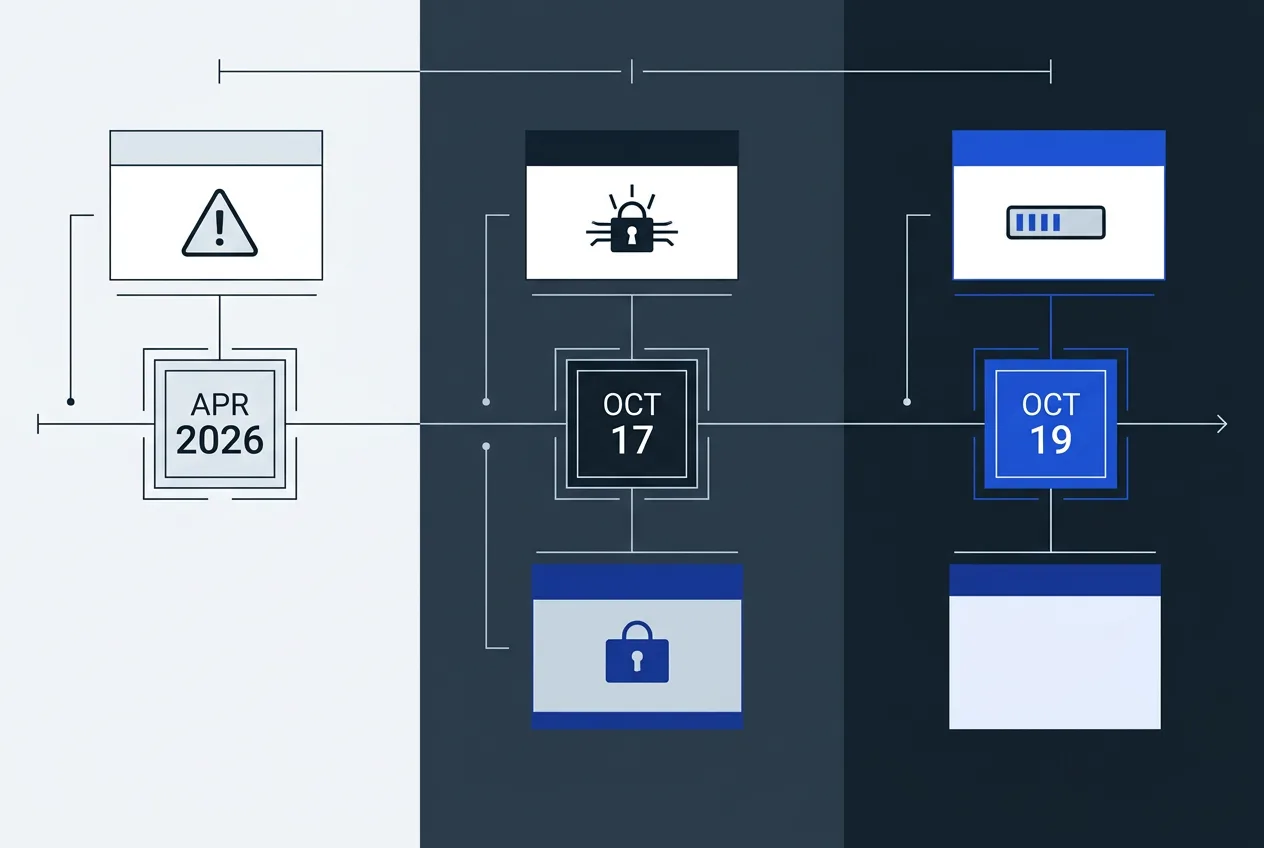
Company officials detected unusual activity on the morning of October 19 and suspended all services at 3:50 p.m. that day. The platform remains offline with no announced resumption date. TrustBank filed a report with Japan's Personal Information Protection Commission on October 20 and plans to notify police on October 21. It has engaged external experts to determine the full scope and root cause while increasing monitoring and security controls.
Users are advised to change any reused passwords on other sites and to remain alert for phishing attempts. The company issued a public apology and stated it will provide further updates once the investigation yields more precise information.
Timeline of Events and Prior Incidents
Access to the system was first compromised on October 17, 2026. Detection occurred two days later, followed by immediate service suspension. This marks the third security-related event at TrustBank in 2026. In April, an unauthorized login incident affected roughly 2,688 accounts. On October 5, a display glitch on the Amazon Pay integration exposed 254 records.
The October 2026 breach is substantially larger than the earlier events. TrustBank has stated that no secondary harm to users has been confirmed so far, though investigators continue to examine logs and potential data use. The company is a subsidiary of Change Holdings and runs one of Japan's largest platforms for the furusato nozei hometown tax donation program.
Services will resume only after forensic review confirms safety. TrustBank has not set a target date for restoration.
User Protections and Ongoing Actions
TrustBank recommends that affected individuals monitor their email and accounts for unusual activity. It encourages the use of unique, strong passwords across all online services. The company has not disclosed whether multi-factor authentication was enabled on the affected systems prior to the incident.
Official communications emphasize cooperation with regulators and law enforcement. Updates on the investigation will be posted on the TrustBank website. Donors who used the platform should watch for official notices from local governments that participate in the furusato nozei system, as some tax-related records may also require verification.
Businesses and individuals relying on Furusato Choice for donation management should consider temporary alternative channels until services return. The absence of payment data in the breach reduces certain financial risks, yet the scale of exposed personal identifiers still requires careful attention to identity protection.
Frequently asked questions
What information was exposed in the TrustBank breach?
The breach exposed names, email addresses, physical addresses, telephone numbers, hashed passwords, and estimated donation tax-deduction amounts for 4.45 million records. Payment card details were not included.
When did TrustBank detect the unauthorized access?
Unusual activity was detected on the morning of October 19, 2026. The breach itself occurred on October 17, and services were suspended later that day.
Has TrustBank announced when services will resume?
No resumption date has been set. The company stated that services will return only after external experts complete the forensic investigation and confirm system safety.
What should users do after the Furusato Choice incident?
Users should change any reused passwords on other sites and monitor accounts for suspicious activity. TrustBank has advised watching for phishing attempts that might reference the breach.
TrustScope
Comments 10