
Zeabur Security Review: Environment Variable Exposure in Two 2026 Breaches
In short
Two security incidents in 2026 exposed millions of environment variables on Zeabur before the platform announced its full shutdown by December 31.
Zeabur security review reveals repeated failures in credential handling that exposed sensitive data for more than 321,000 accounts. The Taiwan-based deployment platform confirmed two separate incidents in 2026 that involved environment variables containing API keys, database passwords, and cloud credentials. Platform founder Yuanlin Lin announced on October 17 that all services would shut down by December 31, 2026.
The incidents occurred on August 27–28 and October 14–15. Attackers gained access to shared clusters across nine regions and read production databases, including 3,218,965 environment-variable records. Zeabur stated that some long-lived internal credentials were stored in plaintext and had not been rotated after the first breach.
Timeline of Zeabur Security Incidents and Shutdown
The first confirmed breach took place in late August. An attacker exploited a vulnerability in a user-deployed public service, escalated privileges, and accessed parts of the production database. Zeabur shut down its AI Hub service on September 22 as a defensive step and published a full incident report. Credentials were rotated and some security upgrades were applied at that time.
The second breach occurred on October 14–15. Attackers used internal credentials that remained from the August incident or were stored in a private config repository. They accessed shared clusters, some dedicated GCP servers, and read data from 865 database services. The platform confirmed that 321,810 accounts and 566 plaintext zSend API keys were affected. Investigation reports were released on October 19 and 20.
Zeabur halted new dedicated server purchases immediately after the October announcement. Dedicated server renewals stopped on December 1, and all shared clusters and dedicated servers will be permanently shut down by December 31. Users must submit balance refund requests by November 30 and can transfer purchased domains themselves.
Impact on Environment Variables and User Credentials
The October incident exposed environment variables across shared clusters and dedicated servers. Affected data included API keys for AI services, database credentials, and cloud access tokens. Zeabur reported that 11,536 platform access tokens were also compromised, though these were stored as hashes and have since been revoked.
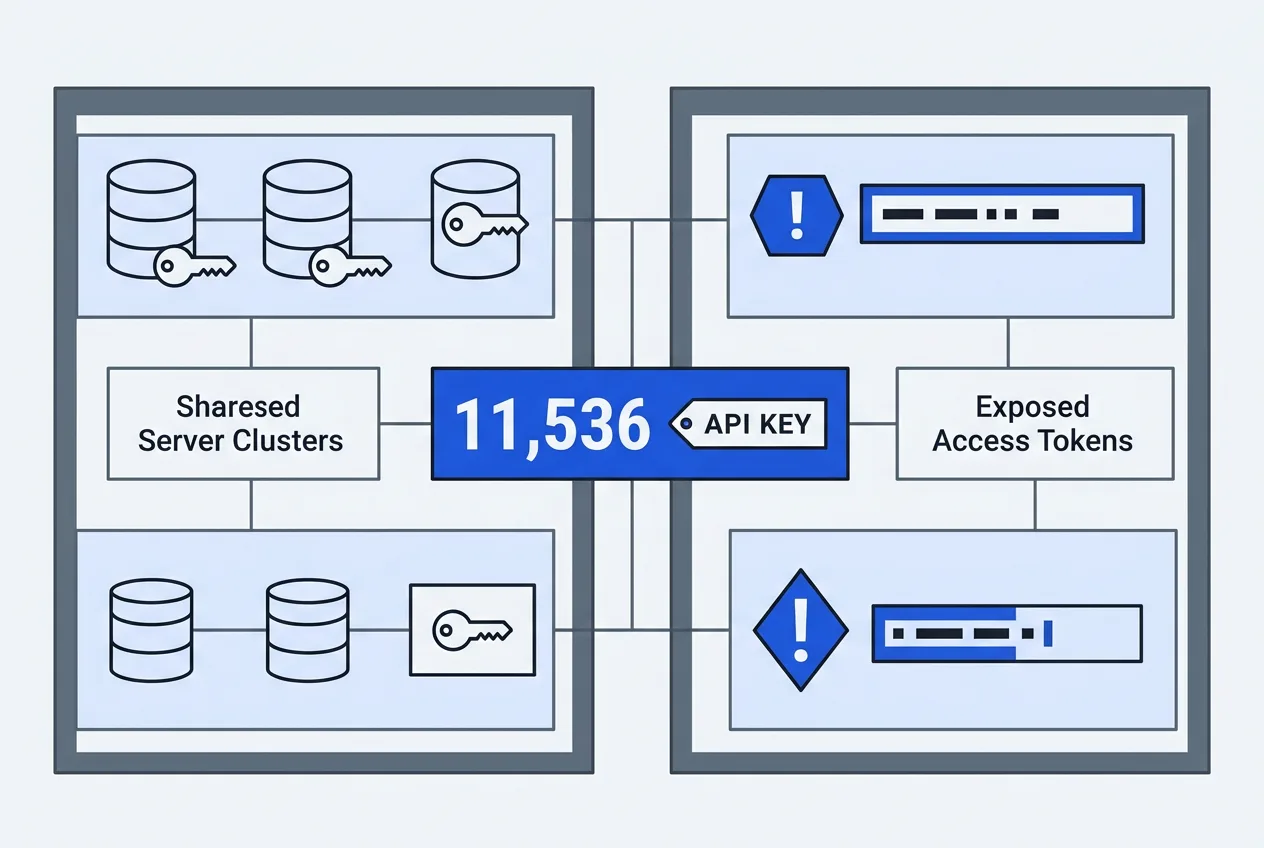
Root causes listed by the company include long-lived admin credentials stored in plaintext, incomplete rotation after the August incident, and over-privileged accounts with publicly exposed management interfaces. No confirmed sales of the full database on dark-web markets have been reported as of October 23.
| Metric | August 2026 Incident | October 2026 Incident |
|---|---|---|
| Accounts affected | Partial database read | 321,810 |
| Environment variables exposed | Portions of production DB | 3,218,965 |
| Plaintext keys compromised | Not specified | 566 zSend keys |
| Database services accessed | Not quantified | 865 services |
Users are advised to rotate every password, API key, and secret that was previously stored in Zeabur environment variables, regardless of prior rotation after August. GCP dedicated server owners must change root passwords and remove any unrecognized SSH keys. Migration of services and data should begin immediately to meet the December deadlines.
Practical Steps After the Zeabur Shutdown Announcement
Account holders can request refunds for remaining balances through Zeabur support tickets until November 30. Security incident loss claims follow a separate process with the same deadline. The company has offered migration assistance, though specific timelines for final data export and deletion remain to be announced.
Developers who relied on Zeabur for quick AI and application deployments now face the task of moving workloads to alternative platforms before shared clusters are paused on December 1. Monitoring for unauthorized access to previously exposed credentials should continue for several months after the final shutdown date.
Frequently asked questions
What data was exposed in the Zeabur breaches?
The October 2026 incident exposed 3,218,965 environment-variable records containing API keys, database passwords, and cloud credentials across 321,810 accounts. The August incident also allowed access to portions of the production database.
When will Zeabur services stop operating?
Shared cluster services pause on December 1, 2026. All dedicated servers and remaining clusters shut down permanently by December 31, 2026.
What should users do with exposed credentials?
Rotate every password, API key, and secret previously stored in Zeabur environment variables. GCP server owners must also change root passwords and remove unknown SSH keys.
Can users still request refunds from Zeabur?
Account balance refunds must be requested via support tickets by November 30, 2026. Security incident loss claims follow a separate process with the same deadline.
TrustScope
Comments
No comments yet. Be the first!