
Bithumb Security Review After October 2026 Internal Mobile System Incident
In short
Bithumb reported unauthorized access to an internal staff collaboration tool on October 27, 2026, with no effect on trading systems or customer assets.
Bithumb security review centers on the October 27, 2026, intrusion into the exchange’s internal mobile groupware system. The platform, a third-party tool called Daou Office, handled staff messaging and file sharing but remained isolated from trading engines, wallets, and customer databases. No funds or crypto assets were moved, and Bithumb confirmed that core services continued without interruption.
Timeline and Technical Details of the Access
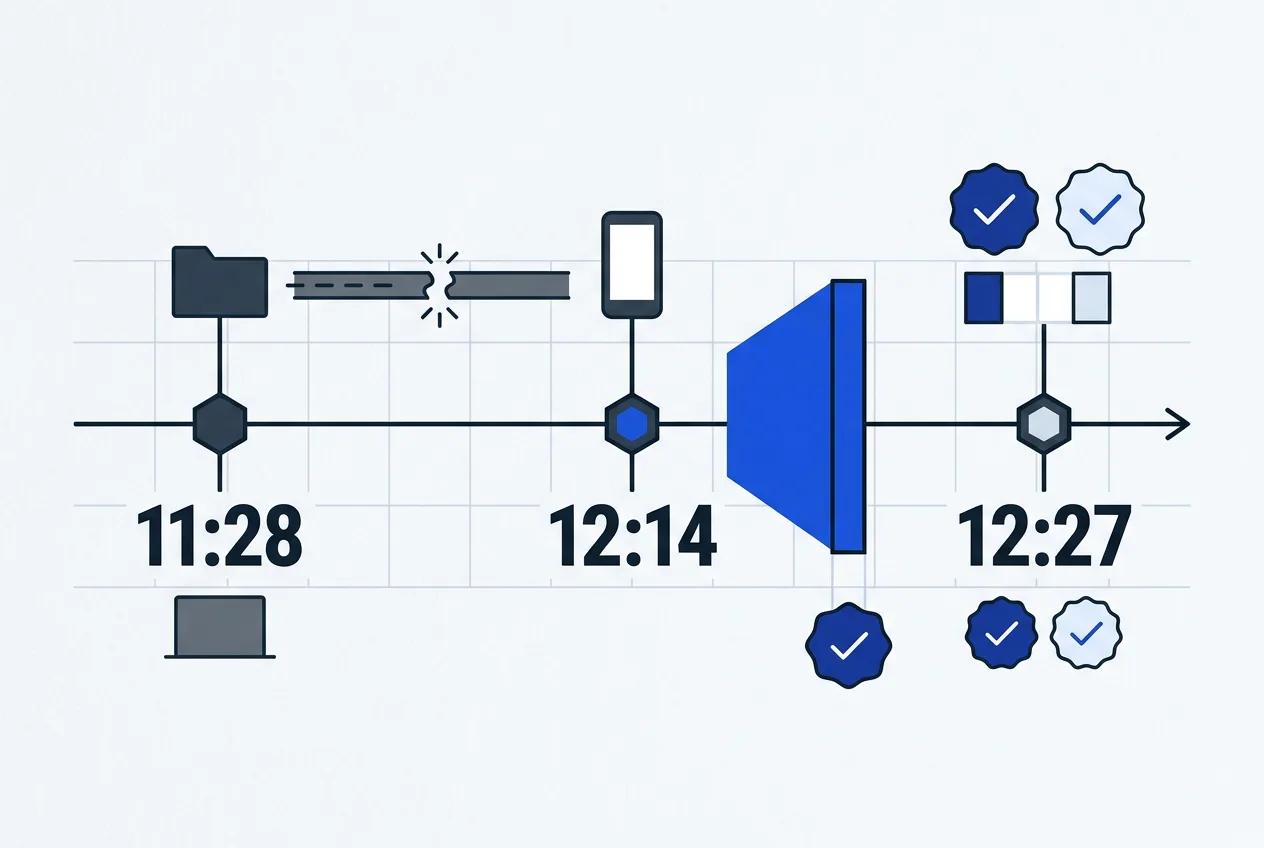
Attackers gained entry between 11:28 and 12:27 KST. Bithumb staff detected unusual activity at 12:14 and immediately blocked the route before suspending the system entirely the same day. The company notified the Korea Internet & Security Agency on October 27 and the Personal Information Protection Commission on October 28. Regulators from the Financial Supervisory Service later began on-site inspections that remained active into late October.
Investigators have not released the precise entry method, though reports point to a vulnerability in the third-party groupware. The system stored encrypted and DRM-protected files for 5,600 customers; these remained unreadable. Readable records for 844 customers included names, mobile numbers, emails, resident registration numbers, driver’s license numbers, bank account details, and ID copies. Data of 715 employees and partners also appeared in the leak, bringing the total affected to roughly 7,159 individuals.
Customer Notification and Compensation Steps
Bithumb began contacting affected users on October 29 and established a dedicated hotline at 1661-5566. The company warned customers about possible follow-on phishing attempts and stated it would cover verified economic losses. CEO Jae-won Lee issued a public apology and announced plans for a full security audit of internal tools, including external expert reviews.
Regulators held an emergency meeting on October 28 and stressed the need for full compensation where losses are proven. Bithumb added extra monitoring for irregular withdrawals and trading activity. As of November 2, 2026, no further incidents have been reported and the exchange continues to operate its trading platform normally.
- Physically separate infrastructure protected trading and wallet systems
- Only the staff groupware tool was reached
- Encrypted files stayed inaccessible to the intruder
- Notifications and a hotline opened within 48 hours
Frequently asked questions
Did the October 2026 incident affect Bithumb customer funds or trading accounts?
No. The accessed system stayed separate from trading platforms, wallets, and asset storage. Bithumb confirmed no theft of funds or crypto occurred.
What personal data was exposed in the Bithumb groupware access?
Readable records for 844 customers included names, phone numbers, emails, resident registration numbers, driver’s license numbers, bank accounts, and ID copies. Another 5,600 customer files remained encrypted.
How is Bithumb handling customer support after the incident?
The exchange started direct notifications on October 29 and opened hotline 1661-5566. It pledged compensation for any verified secondary financial harm.
Are regulators still reviewing Bithumb after the October 2026 event?
Yes. The Financial Supervisory Service began on-site inspections in late October that were ongoing as of November 2, 2026.
TrustScope
Comments
No comments yet. Be the first!