
Fore Coffee review: Metabase Platform Data Access Incident Analysis
In short
Up to 5.7 million customer accounts were potentially exposed through unauthorized access to Fore Coffee’s Metabase platform between October 19 and 27, 2026.
Unauthorized access to PT Fore Kopi Indonesia Tbk’s Metabase analytics platform occurred between October 19 and 27, 2026. The incident potentially touched 5.7 million customer accounts, though the exact number of records viewed remains under investigation. Payment card details and national ID photos stayed outside the affected dataset.
Timeline and technical response to the Fore Coffee data breach
Fore Coffee detected unusual activity during an internal review that ran from October 19 to 27. Staff revoked the unauthorized accounts and secured the platform within 24 hours. They updated Metabase to the current release, applied available patches, and enabled two-factor authentication for logins from new devices.
The company appointed an independent forensic consultant to examine the scope of access. It also notified Indonesia’s Ministry of Communication and Digital Affairs. As of October 29, 2026, no confirmed misuse of the exposed data had surfaced in public reports or company statements.
CEO Vico Lomar issued a public apology and directed customers to reset PINs and avoid sharing one-time passwords. The firm continues to monitor for suspicious activity and has opened a dedicated email channel for privacy inquiries.
Metabase security review and data exposure details
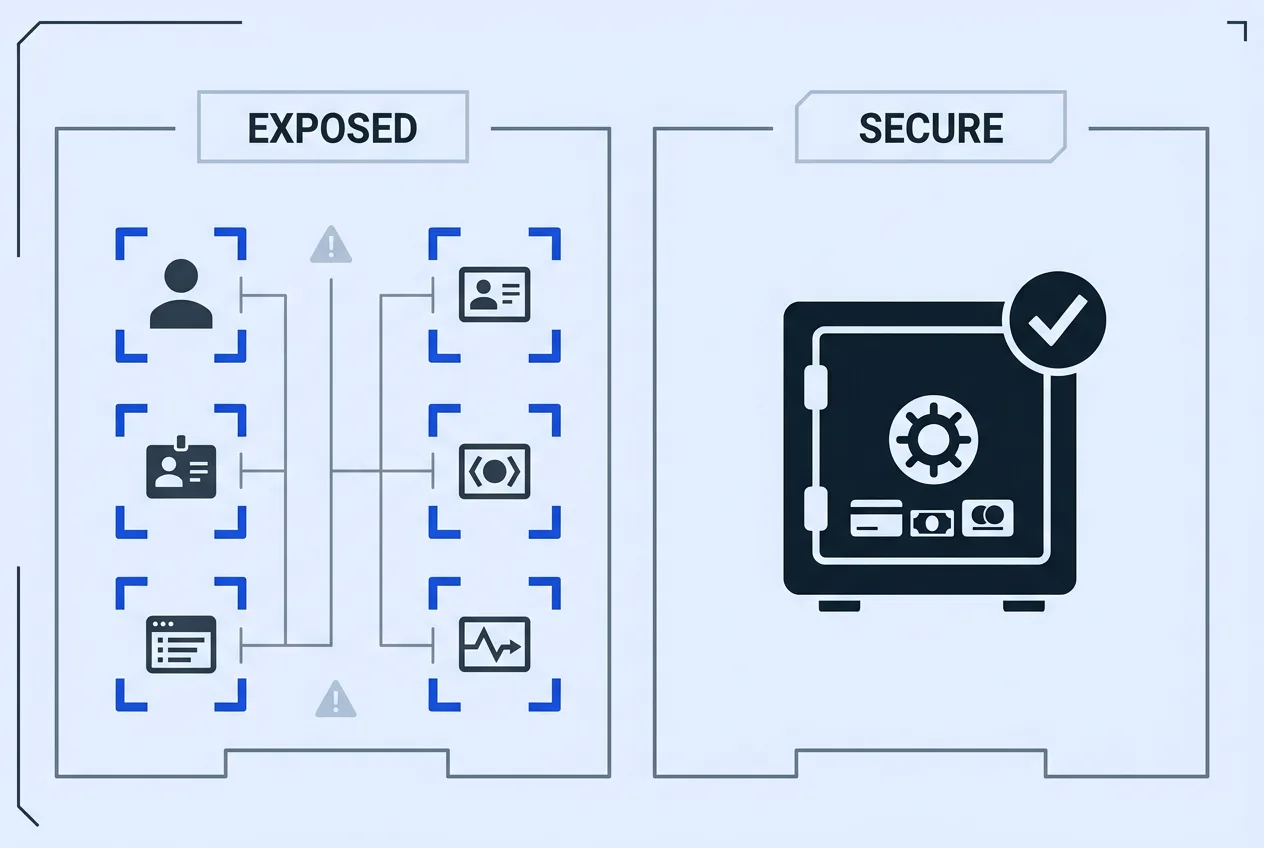
The compromised system stored names, email addresses, phone numbers, dates of birth, gender information where supplied, delivery addresses, and purchase histories. Hashed PINs were also present. No full payment credentials or national ID card images were held in the Metabase instance.
Metabase has recorded critical vulnerabilities in the past, including a zero-day SQL injection issue disclosed in August 2026. Public sources have not confirmed whether the Fore Coffee incident exploited a known flaw or relied on compromised credentials.
Users should treat any unsolicited messages referencing their Fore Coffee account as potential phishing attempts. Monitoring bank statements and enabling app-level alerts remains a practical step until the forensic review concludes.
Practical steps for affected customers
Customers who received direct notification from Fore Coffee should immediately change their app PIN and review recent transactions. Those who have not received notice can still verify account status through the company’s privacy contact.
- Reset PIN inside the Fore Coffee app and avoid reuse across services.
- Watch for unexpected calls or messages asking for OTP codes or personal details.
- Keep records of any unusual account activity and forward them to privacy@fore.coffee.
The company has stated that material updates will be published once the independent investigation produces verified findings. Until that point, the scale of actual data viewing stays preliminary.
Frequently asked questions
What data was exposed in the Fore Coffee incident?
Names, email addresses, phone numbers, dates of birth or gender where provided, registered addresses, purchase history, and hashed PINs were accessible. Payment card details and national ID photos remained on separate systems and were not affected.
How quickly did Fore Coffee respond to the Metabase access?
Staff identified unusual activity during an October 19–27 internal review, revoked the accounts, and secured the platform within 24 hours. They also updated software, enabled 2FA on new devices, and engaged an external forensic team.
Has any customer data been misused after the breach?
As of October 29, 2026, the company reported no confirmed instances of data misuse. The independent investigation remains ongoing and further verified updates are expected.
What should Fore Coffee users do now?
Reset the app PIN, monitor for suspicious contacts, and contact privacy@fore.coffee with questions. Users should also watch account statements for unexpected activity until the full scope is clarified.
TrustScope
Comments
No comments yet. Be the first!