
Giftbit security review after October 2026 dashboard vulnerability incident
In short
An access control flaw in Giftbit’s dashboard allowed limited viewing of customer details on October 23, 2026. The company contained the issue the same day and notified affected accounts.
Giftbit security review focuses on the October 2026 dashboard vulnerability that exposed basic account information for a small number of users. The platform, which issues digital gift cards and rewards through an API, detected and resolved the access control issue within hours. No payment data or passwords were involved.
Giftbit background and security practices
Giftbit operates as a no-subscription-fee service for distributing digital rewards across more than 1,400 brands. Founded around 2011 and based in the Victoria, BC and Calgary area, the company maintains SOC 2 Type II certification, PCI SAQ-D compliance, and GDPR alignment. It uses TLS 1.2 or higher for transit encryption and AES-256 for stored data, along with multi-factor authentication options and continuous monitoring.
Pre-incident user feedback on sites such as Capterra and SaaSworthy averaged 4.5 to 4.6 out of 5. Trustpilot scores showed more variation, primarily around support response times and fraud verification processes. Third-party safety scanners rated giftbit.com as low-risk both before and shortly after the event.
Businesses using the platform for employee incentives or customer promotions rely on its API to issue and track rewards without managing inventory. The service emphasizes direct integration rather than reseller models, which reduces some intermediary risks but places responsibility on the customer to monitor account activity.
October 2026 dashboard incident timeline and scope
On October 23, 2026, at approximately 11:56 a.m. PDT, an attacker exploited an access control vulnerability in one of Giftbit’s web application dashboards. The intrusion granted privileged access to the main admin panel. Giftbit identified the activity at 12:19 p.m. PDT, contained the session, and completed a configuration fix by 5:16 p.m. the same day.
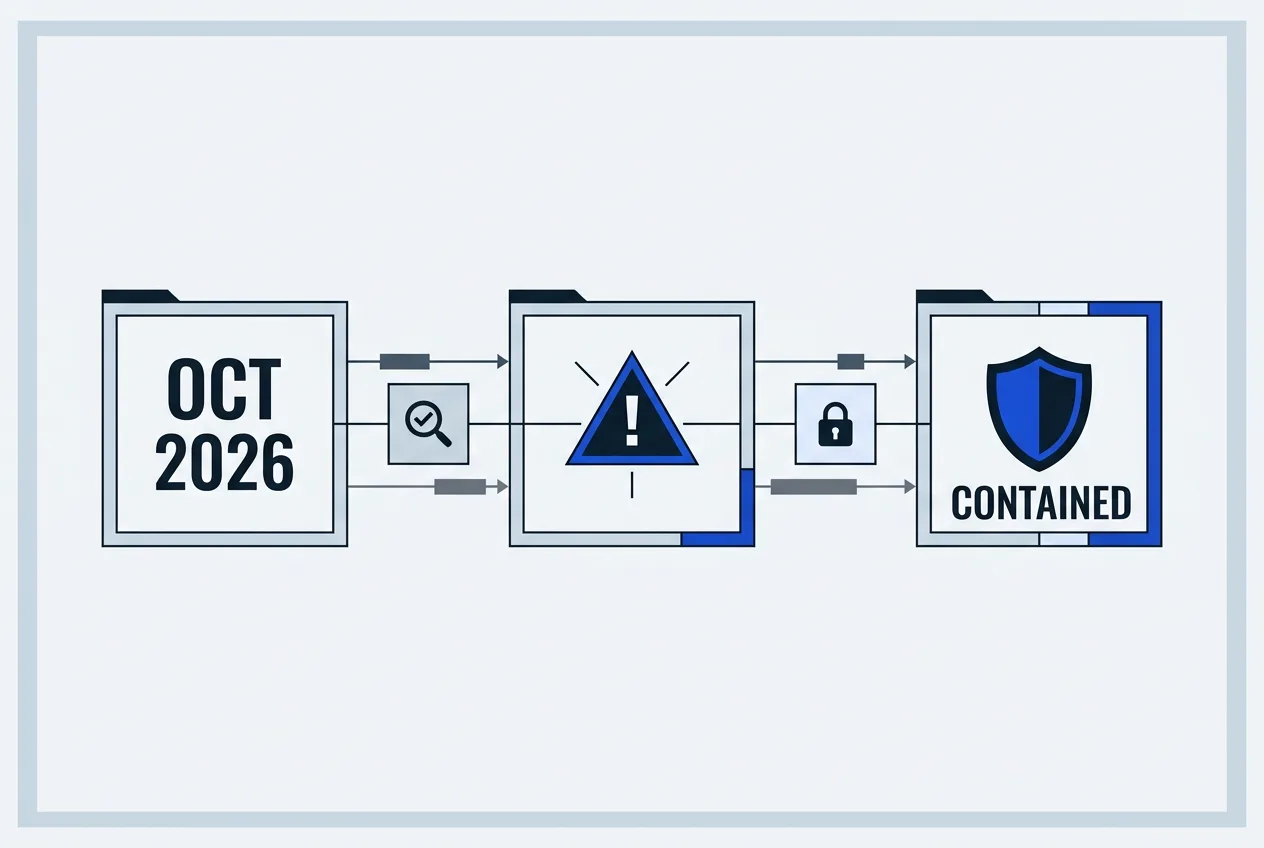
The attacker viewed basic customer account details for 12 accounts, including names and emails. At least 10 of those accounts linked to addresses associated with the attacker. The intruder also saw details on 500 rewards—128 unclaimed and 372 redeemed—plus eight recipient email addresses tied to seven customers. No account balances, payment card information, bank details, or passwords were accessed. The incident did not involve remote code execution or any known PHP vulnerabilities.
Affected customers received direct notifications. Giftbit offered reward cancellations, refunds, or reissues where appropriate. An external security vendor and incident response team were engaged, and the company stated that further updates would appear on its incident page. Users were advised to watch for phishing attempts that might use the exposed names and emails. As of the October 27 update, no confirmed misuse of the accessed data had been reported.
Similar access issues appeared at other gift-card providers during the same period, though each involved separate root causes. Giftbit’s platform and API remained fully operational after the fix.
Current trust signals and recommended user actions
The limited scope of data viewed and the rapid containment reduce the immediate risk profile compared with incidents that expose payment credentials. However, the exposure of names and emails still warrants vigilance against targeted phishing. Customers should verify any unexpected messages referencing Giftbit rewards and avoid clicking links in unsolicited emails.
Organizations evaluating the service should review Giftbit’s ongoing incident page for dated updates and contact security@giftbit.com with specific questions. Those already integrated via API can audit recent reward issuances and confirm that MFA remains enabled on all administrative accounts.
Independent security assessments addressing this specific event were not widely available by October 29, 2026. General site-safety checks continued to classify the domain as legitimate. Companies with strict compliance needs may request the latest SOC 2 report directly from Giftbit before expanding usage.
Frequently asked questions
What data was accessed in the Giftbit incident?
Basic account details for 12 customers and information on 500 rewards were viewed. No payment details, passwords, or account balances were reached.
How quickly did Giftbit fix the dashboard vulnerability?
The company detected the unauthorized access at 12:19 p.m. PDT and completed the configuration patch by 5:16 p.m. the same day.
Should existing Giftbit users change passwords after the incident?
Passwords were not accessed. Users should still confirm MFA settings and monitor for phishing emails that reference their account details.
Is Giftbit still operational after the October 2026 event?
The platform and API remained fully functional. Affected customers received direct outreach for any needed reward adjustments.
TrustScope
Comments 1