
YMIRLINK Security Review: Cuenote FC Data Exposure and Customer Impact
In short
The October 2026 unauthorized access to YMIRLINK's Cuenote FC exposed over 51 million records across 49 dedicated systems. This review details the timeline, scope, and ongoing effects.
YMIRLINK's Cuenote FC email delivery service suffered unauthorized access detected on October 16, 2026. Attackers used a program vulnerability to steal staff credentials and exfiltrate data from 49 dedicated systems. The incident affected organizations across Japan that rely on the platform for bulk email campaigns.
YMIRLINK Security Review: Timeline and Attack Details
Internal detection occurred early on October 16. The company issued its first public notice on October 19 and expanded findings in a second report on October 26. Attackers exploited a library vulnerability, obtained support credentials, installed malicious programs, and pulled data from multiple databases. They also referenced other systems using stolen session information.
The second report confirmed data traces on 49 single-client ASP systems out of 78 targeted. Cumulative records reached approximately 51,628,280, with counts still pending on 16 systems. Three shared systems showed no impact. Cuenote BASE saw a separate exposure of 190 records containing company names, contact details, and emails. Other Cuenote products remained unaffected.
YMIRLINK reported the incident to the Tokyo Metropolitan Police, the Personal Information Protection Commission, and JIPDEC. The company isolated servers, patched vulnerabilities, removed compromised credentials, added IP restrictions, and engaged external experts for monitoring. No confirmed public misuse of the data has been reported, though the firm warned of potential phishing using the info@cuenote.jp domain.
Customer Impact and Data Fields Exposed
Affected clients include retailers, banks, and railway operators that used dedicated Cuenote FC instances for newsletters and member communications. Examples include H2O Persona with roughly 28,052 email addresses and JR Central, JR West, and JR Kyushu exposing Smart EX member emails and IDs. Resona group banks also received notifications.
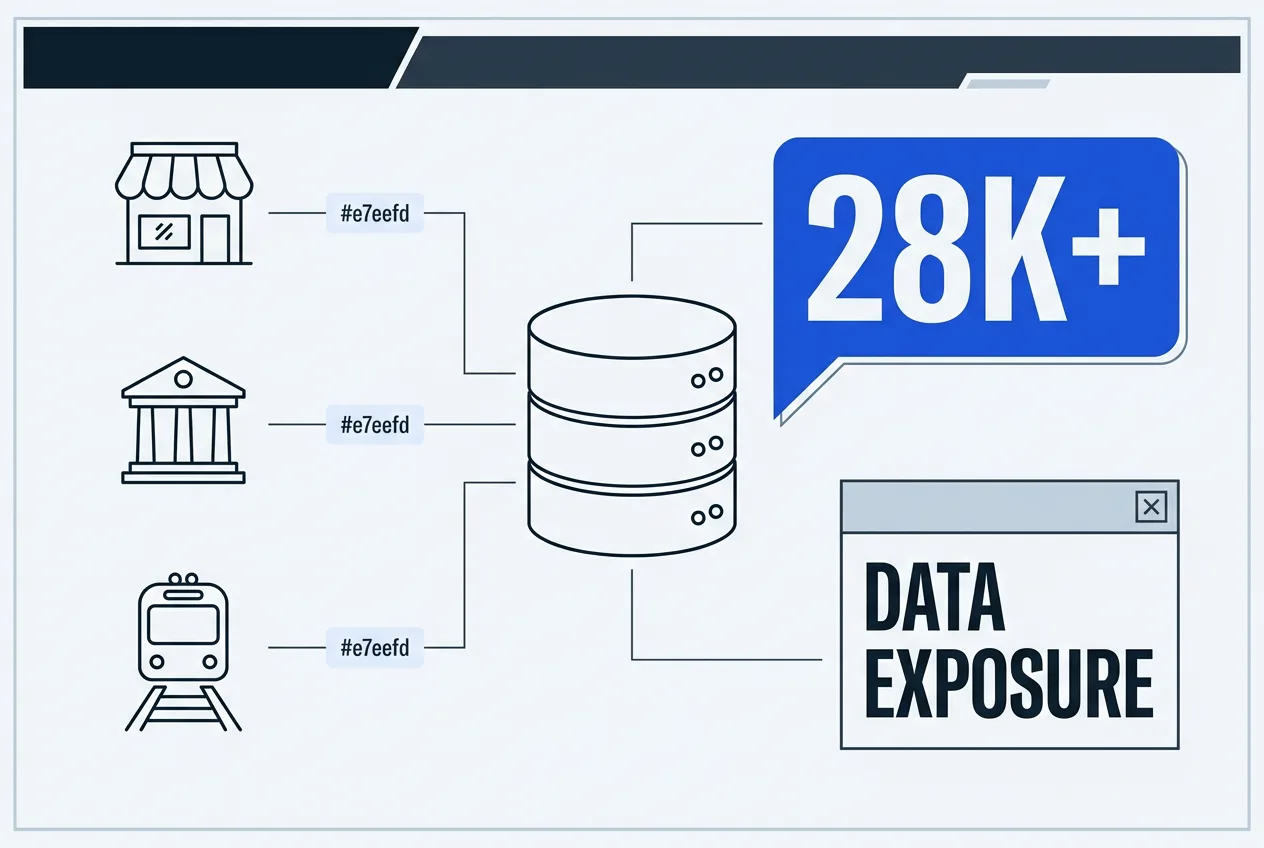
Data fields varied by client system but typically included email addresses plus optional attributes such as names and prefectures. Each client continues individual review of exact exposure. YMIRLINK completed notifications to 42 additional companies by October 26.
Clients such as Cybozu and NTTPC issued their own statements confirming their systems were not directly breached and advised users to watch for suspicious emails. YMIRLINK urged all affected organizations to change passwords and enable two-factor authentication where possible.
Next Steps and Platform Assessment
Investigation continues on the remaining 16 systems and full per-client record counts. YMIRLINK plans further client outreach and end-user notifications where required. Remediation work with external experts is ongoing, along with potential regulatory updates.
The incident underscores supply-chain risks for organizations that outsource high-volume email delivery. Stock in YMIRLINK (TSE Growth: 4372) declined after the initial disclosure. The company stated it is reviewing any material financial impact for fiscal 2026.
Users evaluating the platform should review their own data handling agreements and monitor for secondary phishing attempts. Continued updates from YMIRLINK and regulatory bodies will determine the full scope of long-term effects.
Frequently asked questions
What data was exposed in the YMIRLINK Cuenote FC incident?
Attackers exfiltrated traces from 49 dedicated systems totaling over 51 million cumulative records. Fields typically included email addresses and optional attributes such as names and prefectures, with exact details varying by client.
How did the unauthorized access occur?
Attackers exploited a program or library vulnerability to obtain support staff credentials on October 16, 2026. They installed malicious programs, exfiltrated database data, and attempted further access with stolen session information.
Has any misuse of the exposed data been confirmed?
No widespread public disclosure or confirmed misuse has been reported as of October 28, 2026. YMIRLINK warned clients about possible phishing emails impersonating the cuenote.jp domain.
Which organizations were affected?
Primarily Japanese enterprises using dedicated Cuenote FC instances, including retailers, banks, and railway companies such as JR Central, JR West, JR Kyushu, and Resona group banks.
TrustScope
Comments 2