
ConnectWise Cloud Backup Review After Credential Theft in Microsoft 365 Tenants
In short
The October 2026 incident exposed Microsoft 365 tenants through stolen app credentials in ConnectWise Cloud Backup. MSPs must weigh ongoing service suspension against prior backup integrity.
ConnectWise Cloud Backup suffered unauthorized access to its Microsoft 365 application credentials in mid-October 2026. Attackers obtained a client assertion used for app-only authentication, which allowed them to generate Graph tokens and reach customer tenants without triggering user MFA.
Incident Timeline and Technical Details
ConnectWise detected the access around October 14. Token harvesting occurred primarily on October 15 between 06:13 and 08:34 UTC. The activity originated from a single IP address and succeeded against roughly 162 to 173 tenants according to Huntress telemetry, while Microsoft observed attempts on more than 2,250 tenants overall. The campaign has been attributed to the China-aligned group Storm-0940, which leveraged the open-source ARTEX framework for automated reconnaissance and OAuth abuse at rates exceeding 2,900 attempts per minute.
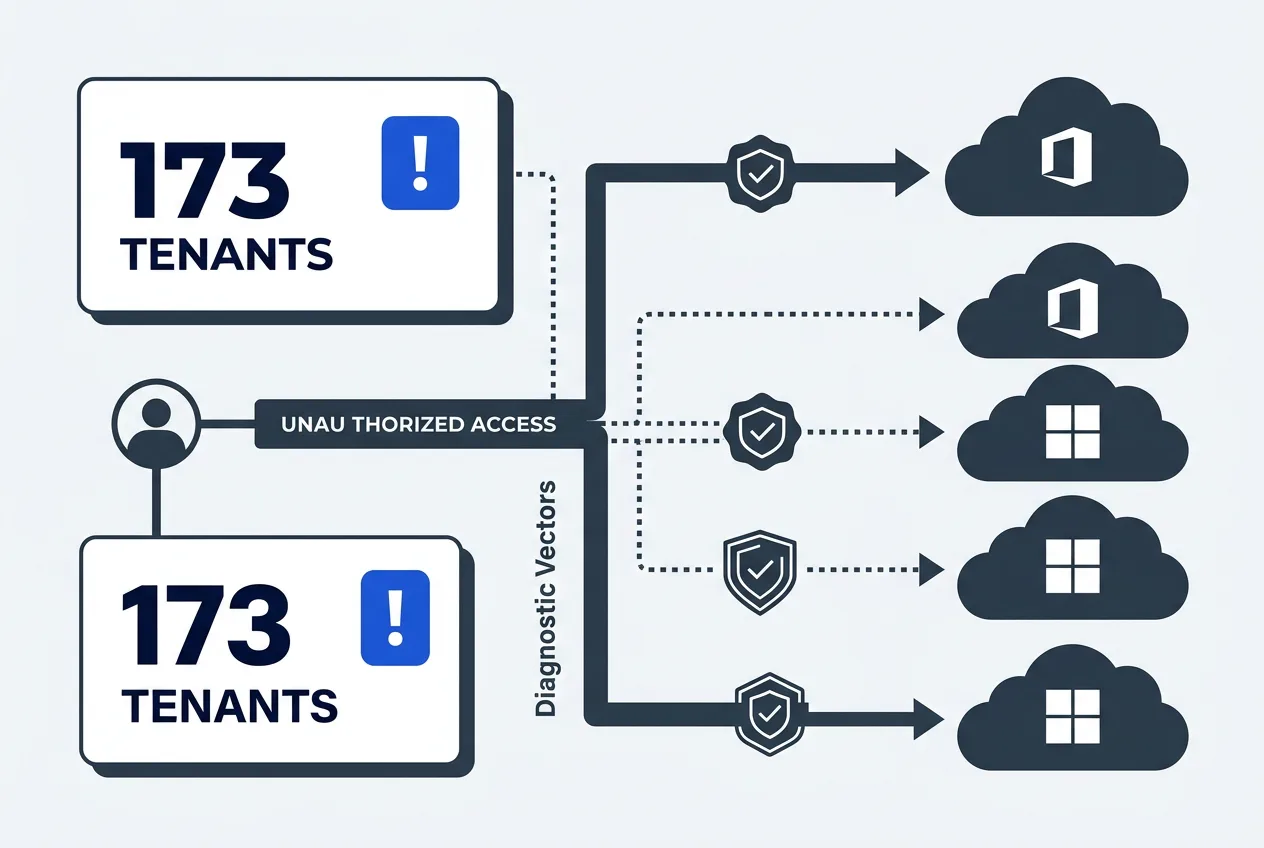
The stolen credential belonged to the ConnectWise Cloud Backup application, formerly SkyKick. It carried broad Microsoft Graph permissions covering mail, files, directory, and related resources. In affected tenants the attacker also observed attempts to self-assign directory roles such as Exchange Administrator and to create long-lived client secrets. No customer-side phishing or misconfiguration was required; the supply-chain vector originated inside ConnectWise’s environment.
ConnectWise responded on October 17 by disabling seven affected app identities and suspending Cloud Backup along with integrated SaaS Security and Cloud Management services. Credential resets and account remediation were completed by October 19. The company stated that existing backup archives remained encrypted and isolated, with no evidence of compromise to the stored data itself.
Current Service Status and MSP Considerations
As of October 28, 2026, Cloud Backup services remain suspended pending third-party validation. ConnectWise has completed internal remediation steps but has not announced a firm restoration date. Partners have been instructed to keep app connections disabled until formal guidance is issued. Phased restoration is expected to begin with restores from existing archives once validation concludes, followed by re-enrollment.
MSPs relying on the service for Exchange, OneDrive, SharePoint, and Teams data face immediate operational constraints. Backup and restore functions are unavailable, forcing organizations to identify alternative short-term solutions. Tenant-specific reviews for persistence mechanisms, including newly added credentials or role assignments, remain necessary even after service resumption.
The incident highlights the concentration of risk when a single multitenant backup application receives extensive consented permissions across many customer environments. Microsoft 365 tenants that used ConnectWise Cloud Backup should audit sign-in logs for the period October 14–17 and verify that no unauthorized directory changes persist.
Security Practices and Next Steps
Organizations evaluating ConnectWise Cloud Backup should monitor the vendor’s Trust Center for phased restoration announcements. Until services resume, administrators can maintain tenant hygiene by reviewing Entra ID sign-in logs, confirming app consent grants, and rotating any client secrets that may have been exposed during the window. Regular validation of backup isolation remains a baseline requirement regardless of vendor.
- Review Microsoft 365 audit logs for the dates October 14–17, 2026.
- Confirm that all ConnectWise-related app registrations are currently disabled.
- Document alternative backup procedures until official reconnection instructions appear.
- Request third-party validation reports once they are released by ConnectWise.
Full impact quantification continues on a tenant-by-tenant basis. MSPs should treat the suspension period as an opportunity to reassess backup architecture and permission scopes before re-enabling any automated connections.
Frequently asked questions
What exactly was stolen from ConnectWise Cloud Backup?
Attackers obtained a client assertion credential for the Microsoft 365 application used by ConnectWise Cloud Backup. This allowed app-only authentication and Graph token generation against connected tenants.
How many Microsoft 365 tenants were actually accessed?
Huntress reported unauthorized sign-ins in 162 to 173 tenants. Microsoft telemetry showed attempts against more than 2,250 tenants, with successful sign-ins observed in a subset of those cases.
Are existing backups still usable after the incident?
ConnectWise states that backup archives remain encrypted and isolated with no indication of compromise. However, restores are unavailable until services are restored following third-party validation.
When will ConnectWise Cloud Backup services resume?
No firm date has been announced. Phased restoration is expected after third-party validation completes, beginning with restores from existing archives.
TrustScope
Comments
No comments yet. Be the first!