
futureshop security review After October 2026 E-commerce Platform Vulnerability Exploit
In short
futureshop experienced multiple access attempts in October 2026 that affected one client store. Details include the scope of data taken and steps taken since.
futureshop security review shows that the SaaS e-commerce platform faced two separate unauthorized access events in October 2026. One incident resulted in the exposure of customer records from a single store. No credit card data was involved in either case.
Details of the October 2026 Access Events
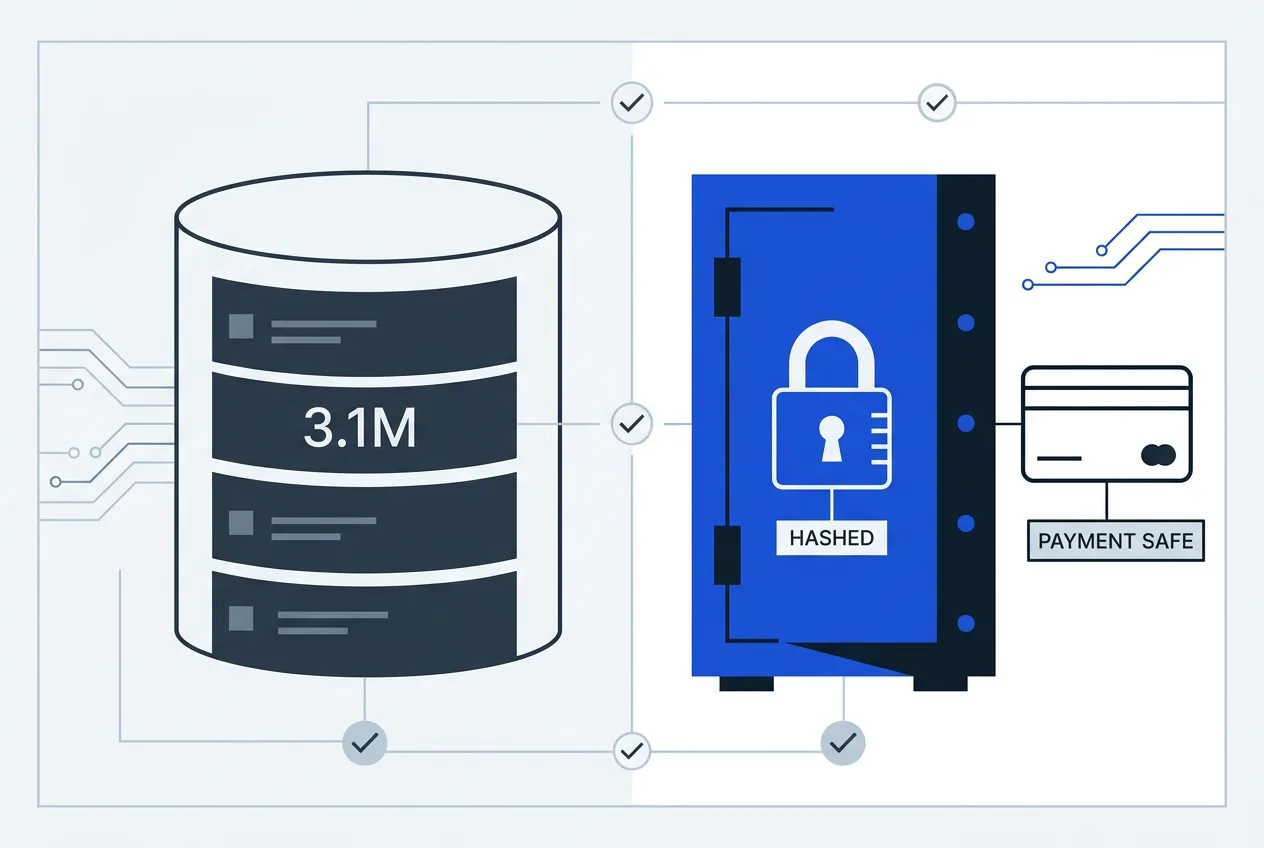
On October 17, an attacker used a server software vulnerability to reach one tenant environment. The affected store was Lindt & Sprüngli Japan. Records for 3,147,377 accounts were taken, later corrected from an initial count of 3,147,469. The fields included member IDs, names, email addresses, postal addresses, birth dates, phone numbers, gender, newsletter preferences, store registration data, and hashed passwords.
Platform staff identified suspicious activity on October 19 through routine monitoring. They blocked the entry point and applied patches that same day. Both futureshop and the affected store reported the event to Japan’s Personal Information Protection Commission on October 23. At the time of the public notice, no confirmed cases of secondary harm had been recorded.
A separate access attempt was detected on October 21 across four servers. One of those servers was a trial environment. Logs showed no evidence of data exfiltration from that event. The platform also performed an emergency shutdown of all sites between October 21 and 22 to address a known PHP vulnerability unrelated to its core code base. Service resumed after server rebuilds and additional hardening measures.
Platform Response and Current Status
futureshop stated that the three October events were unrelated. The company announced plans to strengthen vulnerability management, improve detection systems, and retain external experts for ongoing review. Affected customers at the Lindt store received direct email notices and were required to reset passwords.
The platform itself was established in 2010 and operates as a Japanese SaaS service with headquarters in Osaka. It provides hosted storefronts, management dashboards, and optional CMS modules. User feedback commonly notes responsive support and solid feature sets, while some merchants mention initial setup complexity for advanced configurations.
Operators evaluating the service should review their own data handling practices and confirm current security controls directly with futureshop. External investigation results and any further disclosures remain pending as of November 4, 2026.
Key Facts on Exposed Data and Protections
- Payment card details were never stored on the compromised systems and were processed by a separate payment provider.
- Passwords were stored as hashes, not plaintext.
- The second October 21 event produced no confirmed data loss after log analysis.
- Full platform-wide PHP mitigation required a temporary outage that ended within 26 hours.
| Event Date | Servers Affected | Data Loss Confirmed | Store Impact |
|---|---|---|---|
| Oct 17 | 1 tenant | Yes, 3.1M records | Lindt & Sprüngli Japan |
| Oct 21 | 4 (incl. trial) | No | None reported |
Frequently asked questions
What data was taken in the futureshop October 2026 incident?
The October 17 event exposed member IDs, names, emails, addresses, birth dates, phone numbers, gender, newsletter settings, store registration data, and hashed passwords from one client store. No payment card information was included.
Did futureshop shut down after the October events?
The platform performed a scheduled outage of all storefronts and management interfaces from October 21 evening through October 22 to apply a PHP security patch. Core futureshop services resumed the next day after server rebuilds.
Has futureshop released final investigation results?
As of November 4 2026, futureshop has published initial notices and stated that external experts continue to review logs. Additional findings have not yet been released.
Is futureshop still operating normally?
Yes. All client sites returned to service after the October maintenance window, and the company continues to host new and existing stores while implementing further security controls.
TrustScope
Comments
No comments yet. Be the first!