
MoneySmart Security Review After Late October 2026 Internal Systems Breach
In short
MoneySmart confirmed unauthorized access to internal systems in late October 2026, with some customer data in Singapore and Hong Kong copied by a third party.
MoneySmart security review examines the data incident confirmed on 3 November 2026 after unauthorized access to internal IT systems that began on 29 October. The Singapore-based personal finance comparison platform reported that a third party copied personal data belonging to some customers in Singapore and Hong Kong. Operations continued without interruption while the company blocked access, engaged forensic experts, and notified regulators.
MoneySmart Data Breach Timeline and Scope
The incident involved unauthorized entry into internal systems. MoneySmart discovered the access on 29 October 2026 and confirmed the breach publicly on 3 November. The company stated that the intruder copied selected records but did not access passwords, one-time passwords, or banking or card details. Exact numbers of affected users remain undisclosed; reports describe the impact as limited to “some” customers.
Data elements that may have been copied include names, dates of birth, nationality, personal identification numbers such as Singapore IC numbers, email addresses, mobile numbers, mailing addresses, income ranges, life-stage indicators, details of financial products held, vehicle and insurance information, and application or policy reference numbers. Reward claim records could also include shipping addresses. Exposure varies according to each customer’s prior activity on the platform, such as comparing loans or submitting reward claims.
Media coverage from The Straits Times and Channel NewsAsia on 3 November 2026 aligned with MoneySmart’s statements and noted that no evidence of broader system compromise has surfaced. The platform compares credit cards, loans, and insurance products; the breach occurred against a backdrop of other Singapore data incidents but no attack vector or perpetrator details have been released.
Company Actions and Regulatory Notifications
MoneySmart immediately restricted the unauthorized access, restored system security, and hired independent cybersecurity specialists to conduct forensics. The firm notified Singapore’s Personal Data Protection Commission and Monetary Authority of Singapore, as well as Hong Kong’s Privacy Commissioner for Personal Data and Insurance Authority. CEO Vinod Nair issued a public apology acknowledging customer trust in the handling of financial information.
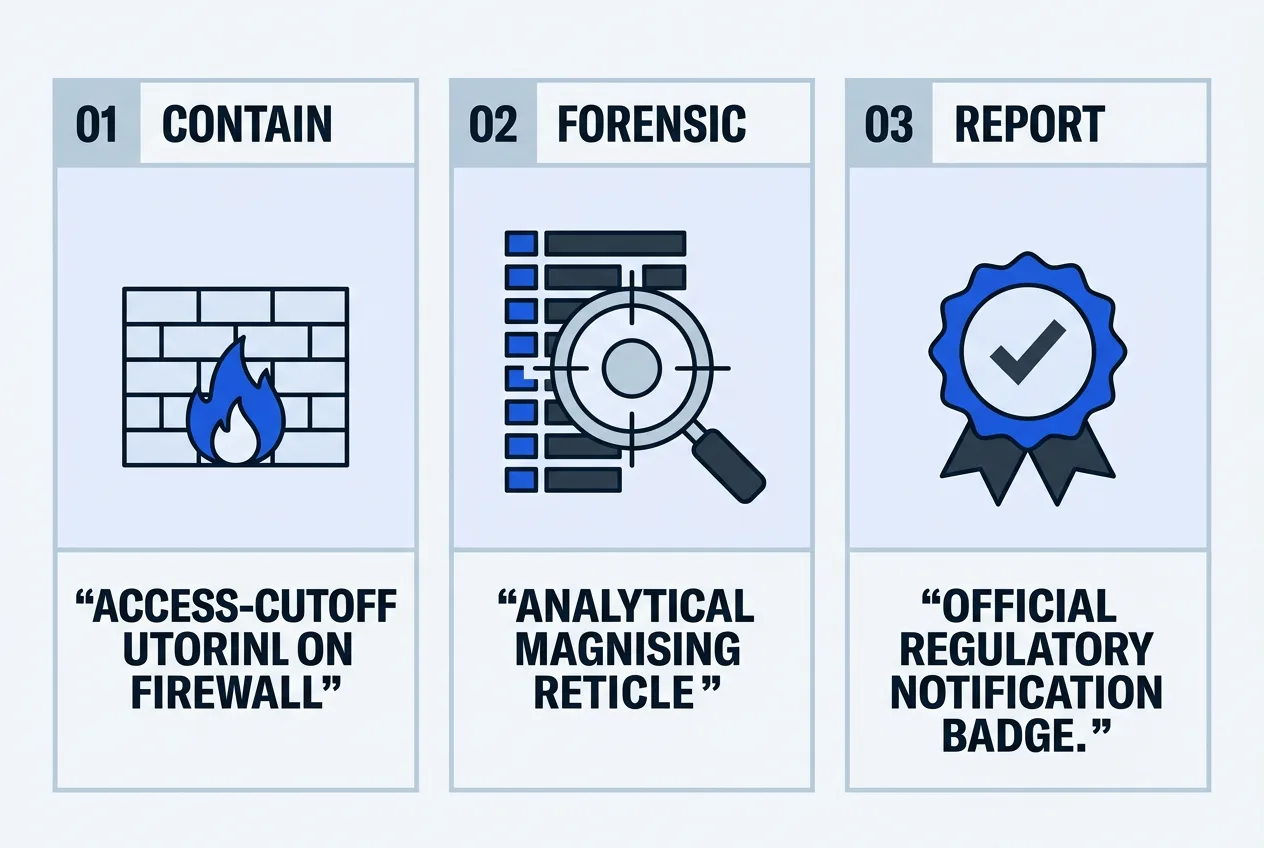
The company stated it is contacting affected customers individually with specific details and recommended protective measures. It emphasized that it will never request passwords, OTPs, or banking credentials by phone or email. Users have been advised to monitor account statements and report suspicious activity to their banks. A dedicated security page on the MoneySmart site provides ongoing updates.
PDPC confirmed it is investigating the incident. No further public timeline for the conclusion of forensics or additional regulatory findings has been issued as of 3 November 2026. The firm indicated it is reviewing internal controls and implementing additional safeguards to reduce recurrence risk.
User Protections and Ongoing Monitoring Steps
Customers should review recent statements from banks and insurers for unusual activity. Those who submitted reward claims or applications through MoneySmart may want to verify that shipping addresses and reference numbers remain accurate. Any unexpected contact requesting credentials should be treated as potential phishing and reported to the platform and relevant authorities.
Because the breach did not involve passwords or banking credentials, immediate account takeover risk appears lower than in incidents that expose login data. Still, the presence of personal identification numbers and financial product details creates potential for targeted fraud or identity misuse. Regulatory investigations may produce additional guidance once complete.
Users can check the company’s official security page for direct notifications and updated instructions. Individuals who have not received contact but suspect they may be affected can reach MoneySmart support to confirm their status. Continued vigilance on financial accounts remains the primary recommended action while investigations proceed.
Frequently asked questions
What data was exposed in the MoneySmart breach?
Names, dates of birth, IC numbers, contact details, income ranges, financial product information, and in some cases shipping addresses and policy references were copied. Passwords and banking credentials were not accessed.
Has MoneySmart notified regulators?
Yes. The company reported the incident to Singapore’s PDPC and MAS as well as Hong Kong’s PCPD and Insurance Authority. PDPC is conducting an investigation.
What should affected customers do now?
Monitor bank and insurance statements for anomalies, watch for phishing attempts, and follow any direct instructions sent by MoneySmart. The company is contacting impacted users individually.
Is MoneySmart still operating normally?
Yes. The platform continues to function without reported service disruptions while the forensic investigation and security improvements continue.
TrustScope
Comments 2