
Genesys Security Review After October 2026 CRM and LMS Breach
In short
Genesys detected unauthorized access to its internal CRM and LMS on October 16, 2026, exposing customer contact data while core platforms remained unaffected.
Genesys detected unauthorized access to internal systems on October 16, 2026. The breach involved its Customer Relationship Management platform and Learning Management System, both used for internal operations. Core customer-facing platforms stayed isolated from the incident.
Genesys Security Review: Incident Timeline and Scope
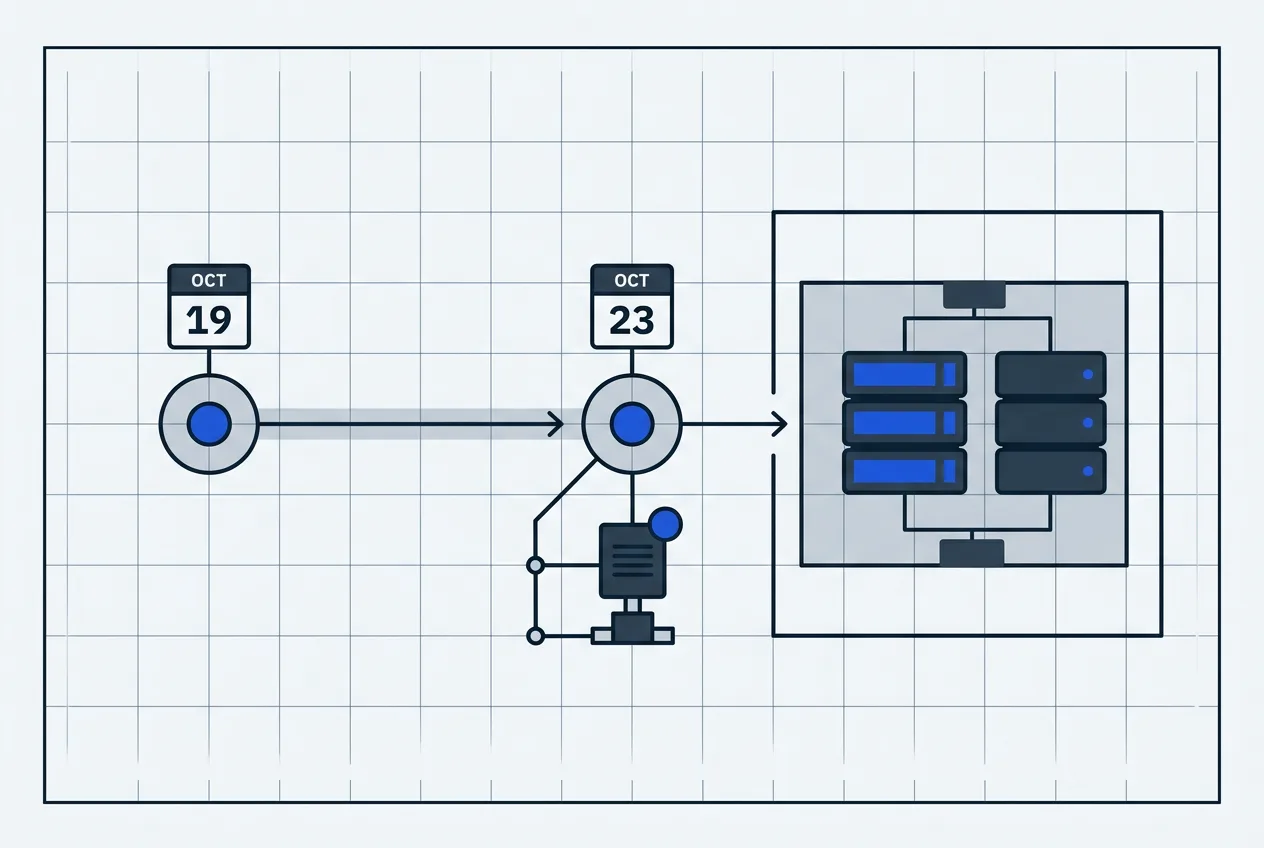
Genesys, a Menlo Park-based provider of contact center software, issued its first public update on October 19. Full containment of the affected systems occurred by October 23, after which the company suspended the LMS. Investigation continued through the end of the month with no confirmed access to production customer environments.
Confirmed data types include names, business email addresses, telephone numbers, job titles, and account interaction records. Exact record counts have not been released by the company. Attacker claims on leak sites reference several million entries, yet Genesys has neither verified nor refuted those figures.
Unaffected systems include Genesys Cloud, Genesys Engage, and Genesys Engage Cloud. No call recordings, analytics data, or partner-hosted environments were compromised. Genesys stated it will not request passwords through unsolicited messages and urged customers to watch for phishing attempts that could leverage the exposed contact details.
Genesys Data Breach Response and Ongoing Risks
Genesys confirmed immediate remediation steps and promised additional updates once the scope review concludes. As of October 31, 2026, no regulatory notification volumes or fines have been publicly detailed. Customers and partners should treat exposed business emails and phone numbers as potential vectors for targeted social-engineering attacks.
Internal systems of this type typically store prospect lists and support records rather than payment information or production credentials. The separation between corporate tools and customer platforms limited the blast radius, a point Genesys emphasized in its statements.
Businesses using Genesys services should review recent inbound communications for anomalies and consider enabling additional verification layers on any accounts tied to the exposed contact data. Monitoring official Genesys channels remains the most direct way to track further disclosures.
Frequently asked questions
What data was accessed in the Genesys October 2026 incident?
Genesys confirmed that names, business emails, phone numbers, job titles, and account records from its internal CRM and LMS were accessed or downloaded. Production customer data stored in Genesys Cloud and Engage platforms remained untouched.
Did the breach affect Genesys Cloud or Engage customers?
No. Genesys stated that customer and partner environments hosted on Genesys Cloud, Genesys Engage, and Genesys Engage Cloud were not reached. Only internal corporate systems experienced the unauthorized access.
What should customers do after the Genesys breach?
Monitor communications for phishing that uses the exposed contact details. Enable extra verification on any accounts linked to those emails or numbers and watch official Genesys updates for further disclosures.
TrustScope
Comments
No comments yet. Be the first!