
HubSpot CRM Review: Data Protection, Compliance and Enterprise Security Practices
In short
HubSpot CRM provides SOC 2 Type II, HIPAA and GDPR compliance with AES-256 encryption and regional data residency options as of late 2026.
HubSpot CRM maintains independently audited security controls and compliance certifications without any reported platform-wide data breaches in 2025 or 2026. Paid accounts receive access to regional data centers and detailed data processing agreements that address GDPR, CCPA and the EU Cloud Code of Conduct. The company publishes SOC 3 reports publicly and maintains a Trust Center for transparency.
HubSpot Security Certifications and Audits
HubSpot holds SOC 2 Type II, SOC 3, SOC 1 Type II added in 2026, HIPAA attestation and multiple privacy certifications including TRUSTe and the EU Cloud Code of Conduct. Annual third-party penetration testing and vulnerability management support these attestations. The public SOC 3 report requires no nondisclosure agreement for access.
Enterprise customers can request the full SOC 1 and SOC 2 reports under standard NDA terms. Subprocessor lists and cyber insurance details appear in the Trust Center. These certifications cover core platform services rather than every third-party integration.
HubSpot publishes a Transparency Report that lists government and legal data requests. In 2025 the company received seven U.S. government requests targeting eight customers and returned mostly subscriber data only. No NSL or FISA orders appear in records through March 2026.
Data Protection Controls and Privacy Practices
Customer data receives AES-256 encryption at rest and TLS 1.2 or 1.3 in transit. Regional data centers operate in the United States, European Union, Canada and Australia. Paid users can request data migration between regions through support.
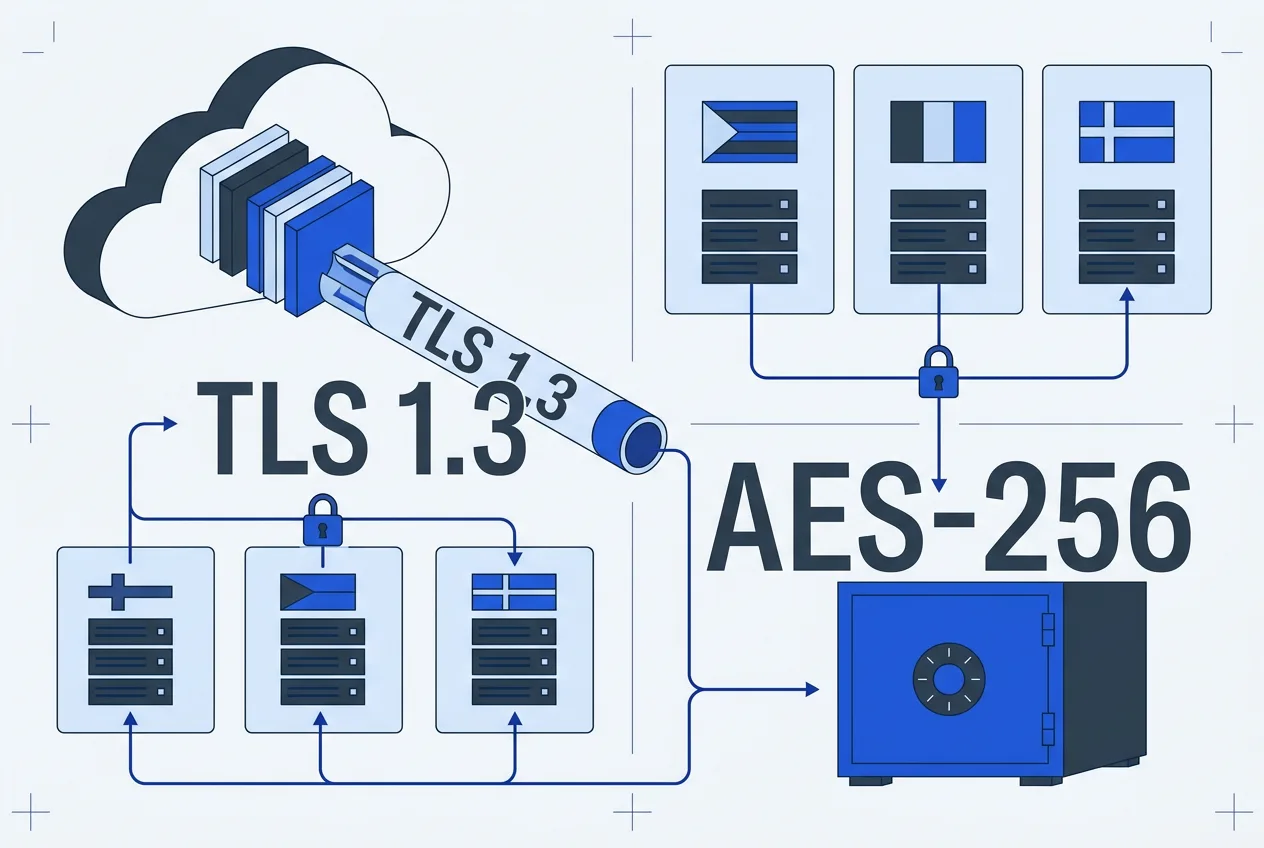
Sensitive Data and Highly Sensitive Data properties add application-layer encryption plus field-level access controls and audit logging. HIPAA support requires the Enterprise tier, explicit opt-in, selection of the Health/Medical category and acceptance of the business associate agreement. Super Admins manage visibility rules.
Consent and subscription management tools allow customers to handle opt-ins and data retention policies. Audit logs remain available for 30 days in the interface and longer through exports. A data processing agreement covers subprocessors, breach notification timelines and standard contractual clauses.
Access Management, AI Controls and User Feedback
HubSpot supports SAML SSO through providers such as Okta and Azure AD, with an option to require SSO for all users. SCIM provisioning and granular permissions cover users, teams, objects and individual properties. The Security Center dashboard lets administrators enforce two-factor authentication and review access patterns.
Administrators control whether customer data reaches AI features. Third-party AI providers are contractually prohibited from training models on HubSpot customer data. An opt-out exists for HubSpot's own model improvement efforts.
User reviews on independent platforms mention pricing and contract terms more often than security incidents. Isolated third-party issues, such as a 2026 OAuth leak at Composio and patched WordPress plugin vulnerabilities, did not compromise the HubSpot core platform. A 2024 incident affected fewer than fifty accounts through limited access attempts.
- Enable Sensitive Data properties before storing regulated information.
- Require SSO and review Security Center alerts monthly.
- Export audit logs regularly for internal compliance records.
- Review the subprocessor list when adding new integrations.
Frequently asked questions
Does HubSpot CRM meet HIPAA requirements?
HubSpot offers HIPAA attestation for Enterprise customers who enable Sensitive Data properties, select the Health/Medical category and sign the business associate agreement.
Where does HubSpot store customer data?
Data centers operate in the United States, European Union, Canada and Australia. Paid accounts can request migration between regions.
Has HubSpot experienced major data breaches recently?
No platform-wide breaches affecting customer data were reported in 2025 or 2026. Isolated third-party incidents did not compromise the core platform.
What encryption does HubSpot use?
HubSpot applies AES-256 encryption for data at rest and TLS 1.2 or 1.3 for data in transit across its infrastructure.
TrustScope
Comments 1