
IDCF Cloud Ransomware Attack October 2026: Impact on 495 Customers and Recovery Options
In short
The October 2026 ransomware incident on IDCF Cloud disrupted services for 495 customers. This analysis covers the attack vector, data exposure findings, and available recovery paths.
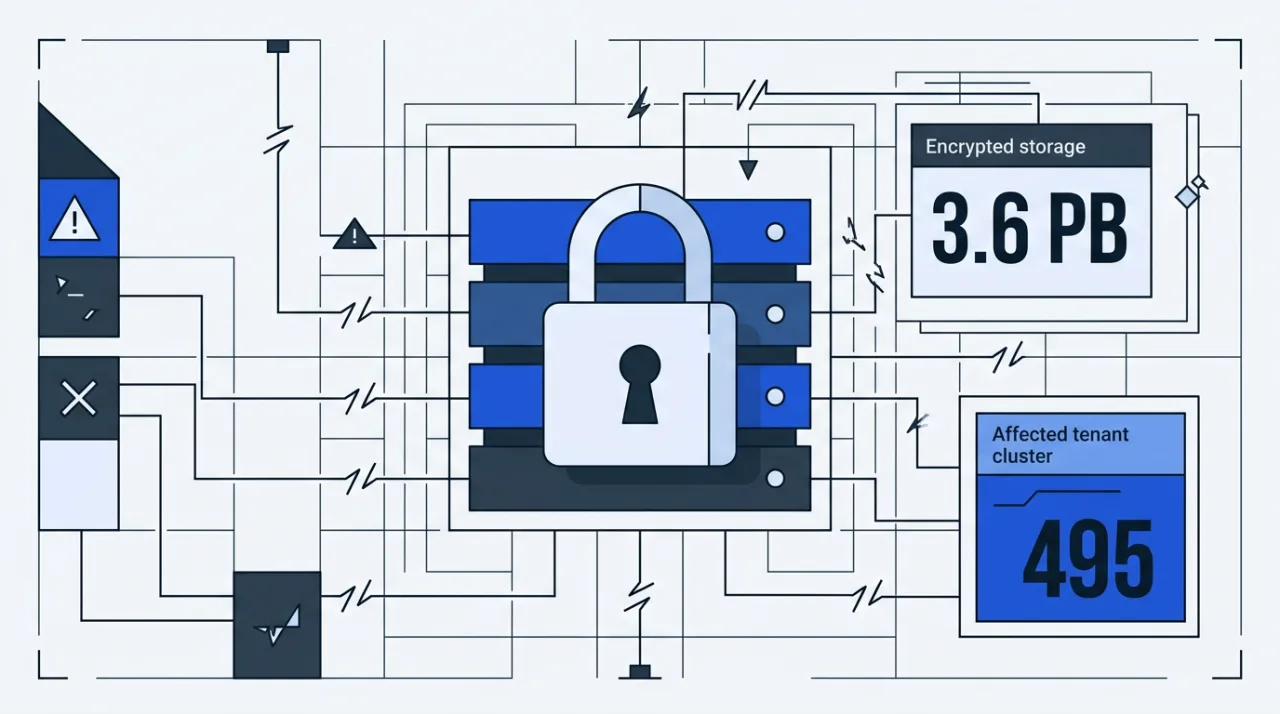
The October 2026 ransomware attack on IDCF Cloud began in the early hours of October 7 and affected four zones in the East Japan Region 1 data center. IDC Frontier, a SoftBank subsidiary, confirmed that attackers used an unpatched vulnerability in the customer portal to gain administrative control over the virtualization layer and encrypt virtual servers. No ransom was paid and no data exfiltration from customer virtual machines has been confirmed.
Services for 495 companies and local governments stopped abruptly. Websites, shipping logistics systems, and email platforms went offline, including operations tied to Ibaraki Prefecture and Nissui. The provider issued seven updates through October 27 with no further material changes reported since the sixth bulletin.
Attack Details and Technical Impact
Attackers reached the virtualization platform through the customer portal login system. They encrypted 225 datastores totaling 3.6 PB and sealed roughly 16,600 virtual machine disks while deleting 554,153 snapshots. The provider has not released the exact software name or CVE identifier, citing ongoing security concerns. The incident remained isolated to the tesla, henry, pascal, and joule zones; TypeS, Private Cloud, and other regions continued without interruption.
Portal registration data for 48 customers was viewed, including company names, login IDs, and hashed passwords. No evidence shows this information left the environment. Several large customers initially flagged possible exposure through email services, but later statements from JR East, JR Kyushu, and Peach Aviation indicated no confirmed leaks after reviewing provider logs.
Recovery Status and Customer Options
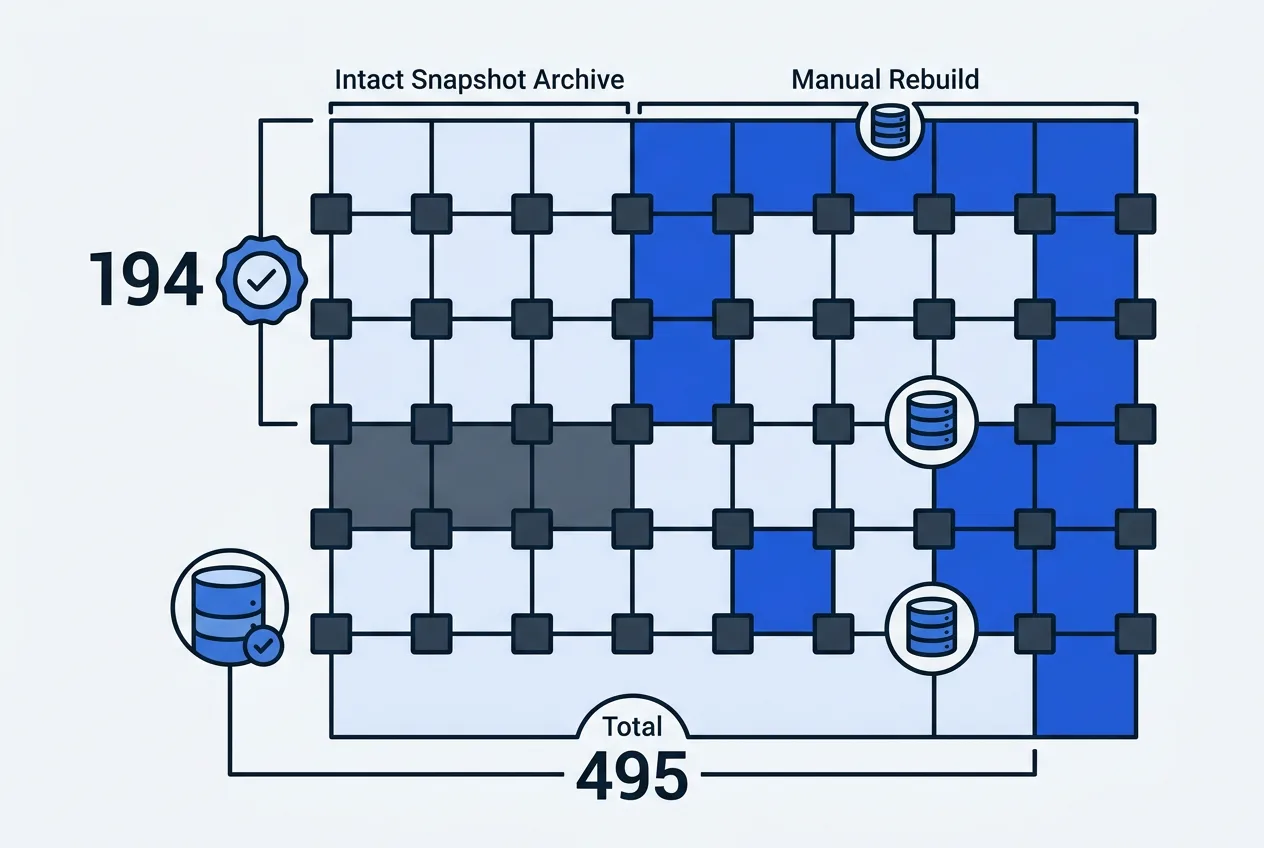
Customers in the affected zones initially received instructions to rebuild from their own backups. On October 14 the provider confirmed that snapshots remained intact for 194 of the 495 organizations and began individual restoration discussions. The remaining 301 customers continue to rely on external backups. Backup services resumed on October 18 for unaffected zones, allowing restores to other clouds or on-premises systems.
IDC Frontier suspended the management console and snapshot features across regions during the investigation. The company plans to rebuild the portal with external identity providers, mandatory MFA, and IP restrictions. No timeline has been given for full restoration of the impacted zones. Customers should verify snapshot availability directly through support channels and maintain offline copies of critical workloads.
- Confirm snapshot status with assigned account manager before attempting restores.
- Test recovery to a different region or provider to avoid single-point dependency.
- Review billing and notification email accounts for any signs of unauthorized access.
- Document all recovery steps for potential insurance or regulatory reporting.
Organizations evaluating IDCF Cloud after the event should compare current security controls against their own risk tolerance and maintain independent backup strategies regardless of provider promises.
Frequently asked questions
Was customer data stolen in the IDCF Cloud ransomware attack?
No exfiltration of virtual server data has been confirmed. IDC Frontier stated that portal registration details for 48 customers were viewed but showed no signs of leaving the environment.
How many customers were affected by the October 2026 IDCF Cloud incident?
Four hundred ninety-five companies and local governments lost access to services in the four impacted zones of East Japan Region 1.
Can affected customers restore data from IDCF Cloud snapshots?
Snapshots were verified as safe for 194 customers. The remaining customers must use their own backups, and snapshot restoration remains suspended pending further investigation.
What security changes is IDC Frontier making after the breach?
The provider plans to implement external identity providers, mandatory multi-factor authentication, and IP restrictions on the rebuilt customer portal.
TrustScope
Comments
No comments yet. Be the first!