
Zeabur Security Review After October 2026 Breach and Shutdown
In short
Unauthorized access between October 14 and 15 exposed millions of records at Zeabur, prompting full platform shutdown by December 31, 2026.
Zeabur suffered unauthorized access between October 14 and 15, 2026, that exposed 3.2 million environment variable records and prompted the platform's complete shutdown by the end of the year. The incident followed an August breach and stemmed from long-lived administrative credentials stored in plaintext. Users must rotate every secret and complete migrations before December 31 to avoid data loss.
Zeabur Security Review of the October 2026 Incident
Attackers used compromised internal credentials to reach shared clusters across nine regions, dedicated GCP servers, and the platform database. Zeabur confirmed that cluster admin tokens created in January 2024 had never expired and remained in a private config repository. Partial fixes after the August incident left several keys unrotated, including shared cluster tokens and certain AWS and GCP credentials.
The company stated that an internal network node added from a compromised GCP server allowed read access to the database. Zeabur published a preliminary report on October 19 and declared the incident resolved on October 20 after revoking credentials and rotating its signing key. Founder Yuanlin Lin accepted responsibility for the root cause in credential handling.
Zeabur also confirmed root sign-ins on 101 GCP dedicated servers belonging to 92 users. Attackers added SSH keys to 50 of those servers and attached 16 customer disk copies to their own virtual machines. Logging limitations prevent full confirmation of how much data was copied from the 865 database services that received read commands.
Data Exposure and User Impact
The breach affected 3,218,965 environment variable records containing both names and values. It also exposed 321,810 accounts with email addresses, usernames, phone numbers, and project metadata. In addition, 566 plaintext zSend API keys and 11,536 hashed platform access tokens were accessed before revocation.
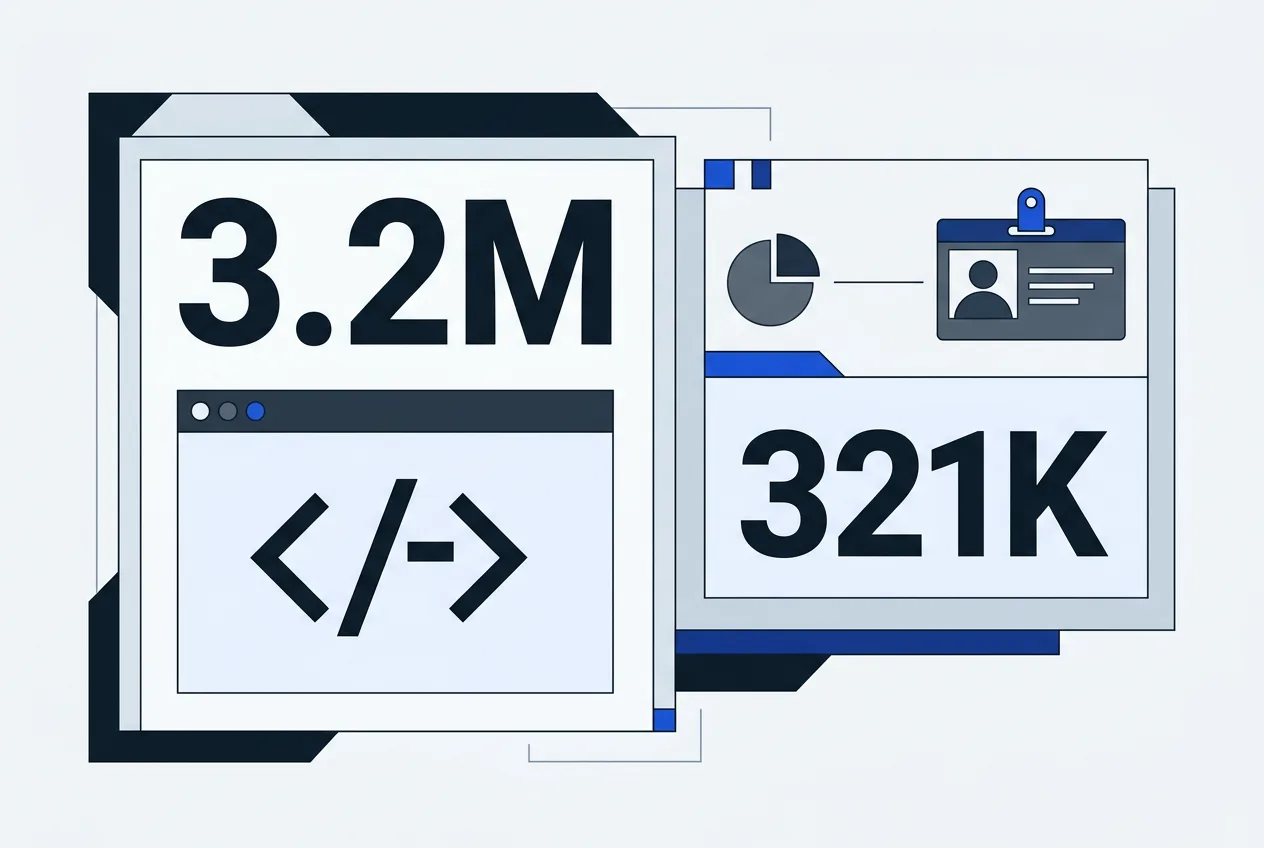
Zeabur advised every user to rotate passwords, API keys, and secrets across all connected services, including third-party providers such as OpenAI and Anthropic. Owners of dedicated GCP servers received instructions to reset root passwords, remove unknown SSH keys, and rebuild from clean images where necessary.
| Incident | Date | Records Exposed | Key Issue |
|---|---|---|---|
| August 2026 breach | August 27, 2026 | Environment variables and production database | User service vulnerability escalated to platform level |
| October 2026 breach | October 14-15, 2026 | 3,218,965 environment variables; 321,810 accounts | Unrotated long-lived admin credentials |
Users can submit claims for losses related to the incident through Zeabur support until November 30, 2026. Refunds for unused service time follow the same deadline. The company has stopped all new dedicated server and domain purchases.
Platform Shutdown Timeline and Migration Steps
Zeabur announced its wind-down in mid-October 2026, citing ongoing security and operational challenges after two breaches within two months. Dedicated server renewals stop on December 1, 2026, and all such servers expire by December 31. Shared cluster services pause on the same date, with limited options for manual backup resumption.
All platform services cease operation on December 31, 2026, followed by data deletion. Zeabur offers migration assistance and recommends that users complete backups and transfers by late November or early December. No further official updates on the investigation have been published as of October 27, 2026.
Frequently asked questions
What data was exposed during the Zeabur October 2026 incident?
Zeabur confirmed exposure of 3,218,965 environment variable records, 321,810 accounts, 566 plaintext zSend API keys, and 11,536 hashed access tokens. The platform also reported root sign-ins on 101 GCP dedicated servers and read access to 865 database services.
When will Zeabur stop all services?
Shared cluster services pause on December 1, 2026. All remaining services end on December 31, 2026, after which data deletion begins. Dedicated server renewals stop on December 1 and expire by December 31.
What should users do after the Zeabur breach?
Rotate every password, API key, and secret connected to Zeabur, including third-party services. GCP dedicated server owners must reset root passwords, remove unknown SSH keys, and rebuild from clean images. Submit any claims by November 30, 2026.
Did Zeabur address the August 2026 breach before the October incident?
Zeabur implemented partial fixes after August 27, 2026, but left several administrative credentials unrotated. The October breach exploited those remaining long-lived tokens stored in plaintext.
TrustScope
Comments
No comments yet. Be the first!