
Sentry Review: Error Tracking, Data Retention and Security Posture
In short
Sentry provides reliable error tracking with defined retention limits and SOC 2 certification, though proper configuration remains essential for privacy.
Sentry serves as a developer platform for real-time error tracking and performance monitoring. Its core strengths include precise error grouping and session replay capabilities. Users evaluating Sentry review often focus on whether its security measures and retention rules align with production needs.
Sentry Review of Error Tracking Features
The platform delivers detailed stack traces, breadcrumbs, and source map support across more than 100 languages and frameworks. Session replay captures user actions leading to crashes, while performance tracing covers Core Web Vitals and distributed spans. The Seer AI agent, expanded in 2025-2026, supplies root-cause suggestions and fix recommendations.
Real-time alerts notify teams of new issues, yet the volume can increase without careful rule tuning. SDKs handle both client-side and server-side event capture. Reviews from 2026 note fast error resolution when integrations with existing tools are set up correctly.
Practical setup involves installing the SDK, configuring source maps, and defining alert thresholds early. Teams that skip initial filtering often face higher noise levels and increased event counts. The free tier supports up to 5,000 errors monthly, which suits small projects before scaling.
- Strong deduplication reduces duplicate reports automatically.
- Session replay limited to 50 events on the free plan.
- Spans and traces scale with usage-based billing.
Data Retention Periods and Pricing Tiers
Default retention varies by plan and data type. Errors stay available for 30 days on the Developer tier and 90 days on Team, Business, and Enterprise plans. Logs, profiles, and metrics follow a 30-day limit across all tiers. Session replays extend to 90 days only on paid plans.
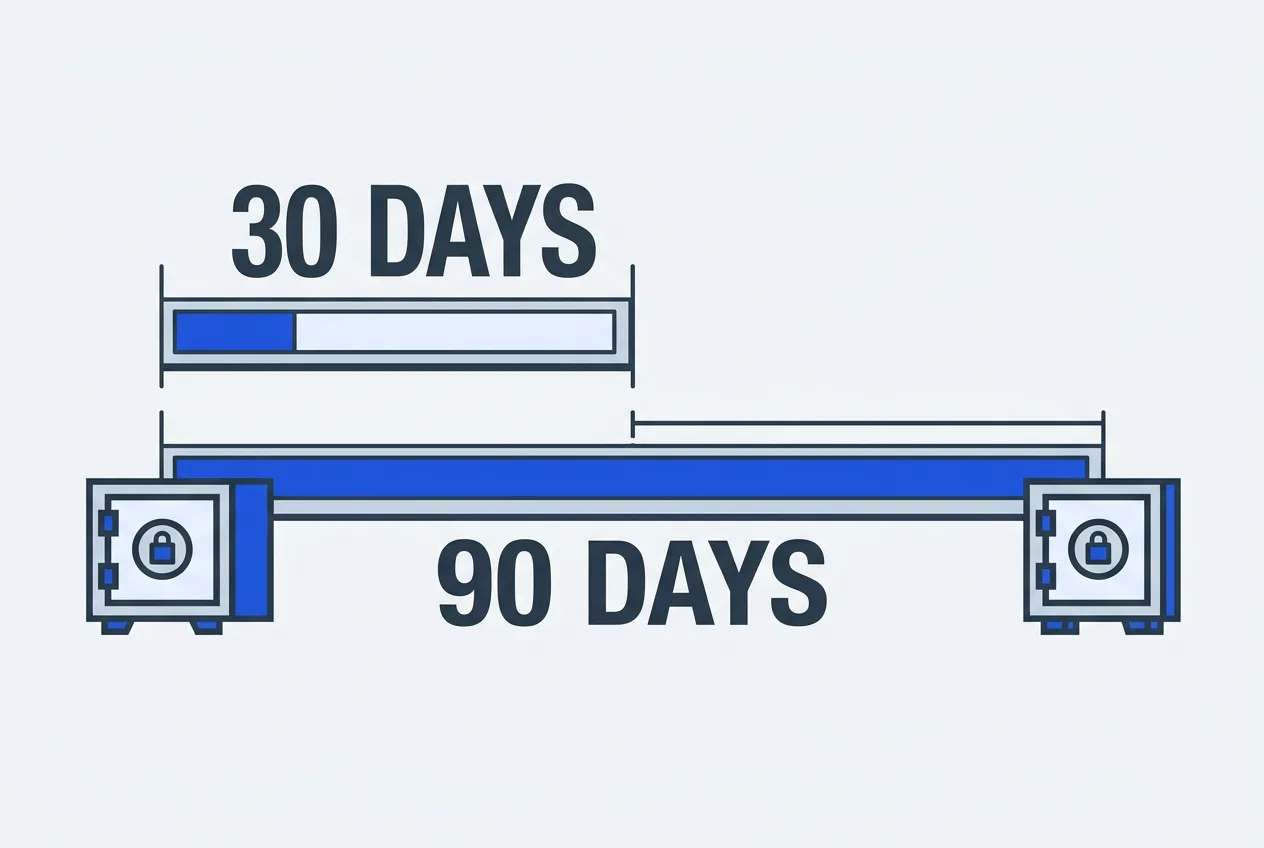
Spans receive 30-day default storage, with Business and Enterprise adding 13 months of sampled data for longer-term analysis. Enterprise customers can request custom retention windows. Account deletion renders data inaccessible within 24 hours, and backups follow the same 30-to-90-day schedule.
| Plan | Monthly Price (annual) | Error Retention | Replay Retention |
|---|---|---|---|
| Developer | Free | 30 days | 30 days |
| Team | $26 | 90 days | 90 days |
| Business | $80 | 90 days | 90 days |
| Enterprise | Custom | Custom | Custom |
Overages follow a pay-as-you-go model once included limits are exceeded. Organizations should monitor event volume closely, as usage spikes directly affect monthly costs. Changes to retention announced in August 2025 took effect for many accounts by November of that year.
Security Posture and Privacy Controls
Sentry runs on Google Cloud Platform infrastructure certified to ISO 27001 and SOC 2 standards. Data remains encrypted in transit via TLS and at rest with AES-256. Field-level encryption options exist for sensitive fields. The company performs annual third-party penetration tests, with summaries available to customers upon request.
Built-in PII scrubbing operates on both client and server sides, and session replay redacts text and images by default. Business and Enterprise plans add MFA, SSO, SAML, SCIM, role-based access, and audit logs. HIPAA attestation and a business associate agreement are available on paid tiers. GDPR and CCPA compliance is supported through a data processing agreement and an EU data residency option.
Recent SDK vulnerabilities, including a critical Next.js middleware bypass fixed in October 2026, were addressed through patches. Self-hosted instances require closer monitoring than the SaaS version. No customer data breaches have been reported, and the company maintains a public security advisory page plus a bug bounty program. Configuration choices determine how much personal data reaches the platform, making initial setup reviews essential for teams handling regulated information.
Frequently asked questions
Is Sentry safe for production error monitoring?
Sentry maintains SOC 2 Type II and ISO 27001 certifications on Google Cloud infrastructure. Annual penetration testing and encryption standards are in place, yet proper PII scrubbing configuration remains necessary.
How long does Sentry keep error data?
Default retention is 30 days on the free plan and 90 days on paid plans for errors. Logs and metrics stay for 30 days across tiers, while Enterprise allows custom extensions.
Does Sentry support HIPAA compliance?
Business and Enterprise plans include HIPAA attestation and a business associate agreement. Organizations must still verify their own data handling practices meet regulatory requirements.
What privacy tools does Sentry provide?
Client and server-side PII scrubbing, session replay redaction, and GDPR-compliant data processing agreements are available. EU data residency options exist for qualifying accounts.
TrustScope
Comments
No comments yet. Be the first!